xkcd 221

Welcome to Lemmy Shitpost. Here you can shitpost to your hearts content.
Anything and everything goes. Memes, Jokes, Vents and Banter. Though we still have to comply with lemmy.world instance rules. So behave!
1. Be Respectful
Refrain from using harmful language pertaining to a protected characteristic: e.g. race, gender, sexuality, disability or religion.
Refrain from being argumentative when responding or commenting to posts/replies. Personal attacks are not welcome here.
...
2. No Illegal Content
Content that violates the law. Any post/comment found to be in breach of common law will be removed and given to the authorities if required.
That means:
-No promoting violence/threats against any individuals
-No CSA content or Revenge Porn
-No sharing private/personal information (Doxxing)
...
3. No Spam
Posting the same post, no matter the intent is against the rules.
-If you have posted content, please refrain from re-posting said content within this community.
-Do not spam posts with intent to harass, annoy, bully, advertise, scam or harm this community.
-No posting Scams/Advertisements/Phishing Links/IP Grabbers
-No Bots, Bots will be banned from the community.
...
4. No Porn/Explicit
Content
-Do not post explicit content. Lemmy.World is not the instance for NSFW content.
-Do not post Gore or Shock Content.
...
5. No Enciting Harassment,
Brigading, Doxxing or Witch Hunts
-Do not Brigade other Communities
-No calls to action against other communities/users within Lemmy or outside of Lemmy.
-No Witch Hunts against users/communities.
-No content that harasses members within or outside of the community.
...
6. NSFW should be behind NSFW tags.
-Content that is NSFW should be behind NSFW tags.
-Content that might be distressing should be kept behind NSFW tags.
...
If you see content that is a breach of the rules, please flag and report the comment and a moderator will take action where they can.
Also check out:
Partnered Communities:
1.Memes
10.LinuxMemes (Linux themed memes)
Reach out to
All communities included on the sidebar are to be made in compliance with the instance rules. Striker
xkcd 221
I thought this has to have been the reference
wtf 🫢️
Oh my God, when I heard about this I figured some super computer was out there breaking encryption, but nope.
public key: 4
::: spoiler secret key also 4 :::
hash salt? Believe it or not, also 4
We have the strongest security in the world because of 4
Fun fact: most implementations actually always use 65537 as the public RSA key (17 was more common earlier, but rare now). It makes computations easier and faster, and doesn't affect security much as long as you pick a hard-to-guess private key. The modulus is the thing that varies in public certificates.
This is only partially true.
RSA public keys consist of two parts:
If the public key were always completely the same, then there would be no point in making different private keys.
Isn't RSA wholly deprecated for like... years by now?
Oh looked it up. It's ssh-rsa that's deprecated because of SHA-1, and NIST wants to phase out RSA-2048 by 2030.
Everyone uses all these huge numbers, so no one is expecting 4. What could go wrong?
"we'll brute force it, but to save some time we'll start at 5 since noone would ever be stupid enough to use a number smaller than that"
This is extremely dumb and stupid, and it made me laugh harder than anything else has in days. Thanks, OP!
Happy to hear you enjoyed it (though full disclosure I did steal it)
My codebase requires guids, so I used 00000000-0000-4000-0000-000000000000
You bonehead! You should have just run a Fourier transform on it.
Not to be mistaken with furry transfem.
my college roommate made this joke in 2009, complete with the '4'
i still don't get it lol
Uh roommate must have predicted the future because this is about a private key for a certificate authority using the number "4" as their whole private key recently. As well as a couple other low digit numbers
EDIT: your roommate might have been talking about this XKCD comic https://xkcd.com/221/
yes! i think so! he was the one who introduced me to xkcd!
Wait, xlcd? One of my laptops had the keys randomly not do what they are supposed to, and some give values like that, but it will give like three of those, than switch to another string to endlessly repeat after that. I don't know what the fuck is going on.
LMAO what? That's wild
I gotcha bud.
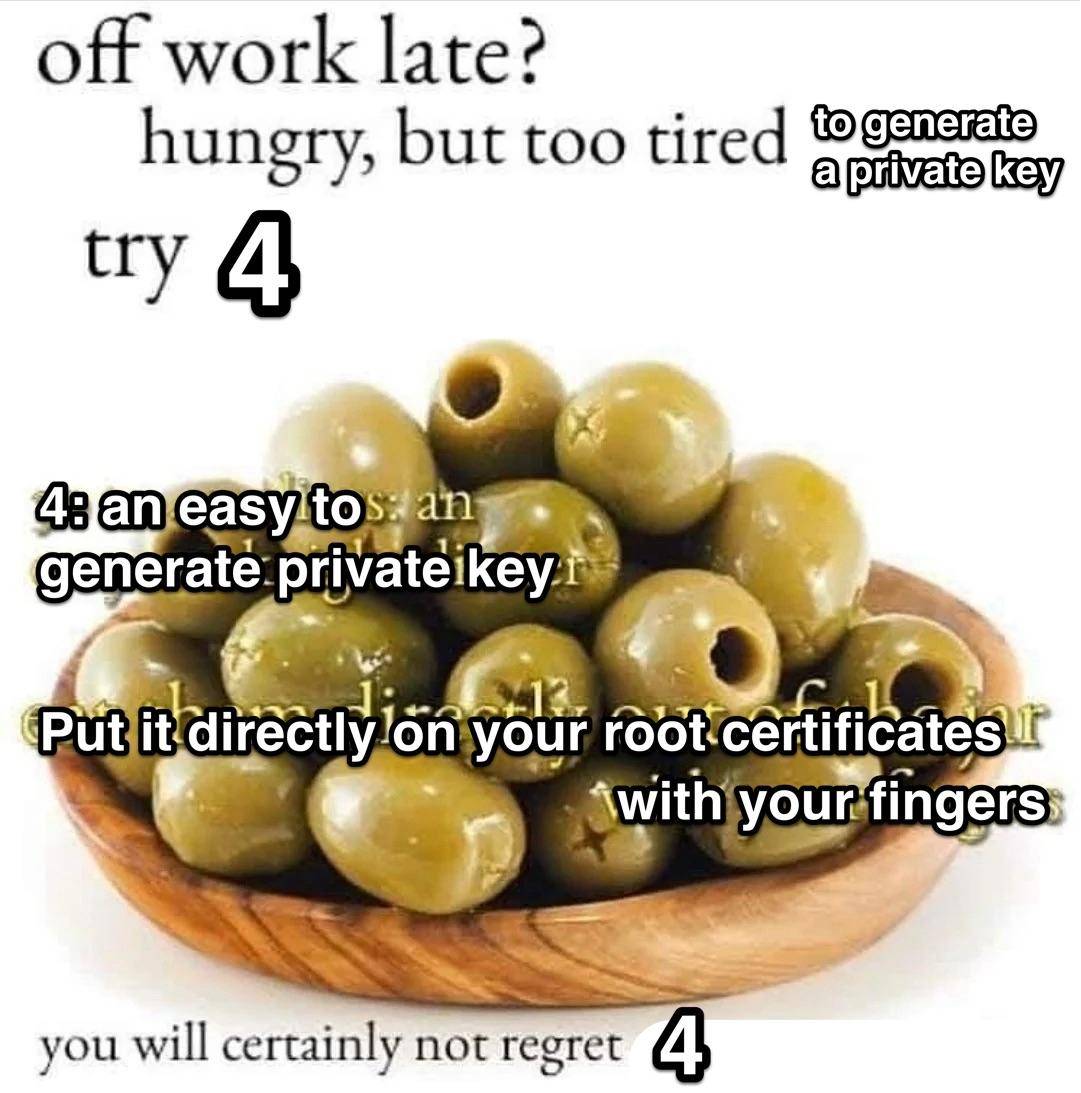
It’s a riff on the olive meme.
https://knowyourmeme.com/memes/hungry-but-too-tired-to-cook-try-30-to-40-olives
256 bit and 512 bit encryption are somewhat common. A 256 bit private key is 64 characters long (I’m simplifying this, don’t @ me about it being hex). A 512 bit private key is twice as long. That long string of random characters is what gives this type of encryption its power. It’s essentially unguessable, even with a computer and a lot of time.
Using “4” as your private key would significantly undermine security. Hackers can’t check every possible option for a 512 bit key, but they can certainly (and trivially) try simple numbers padded by 0’s, like our “4” private key.
You’ve taken a strong and proven system and made it trivially weak. That’s the joke. It’s not that funny, but that’s what you’re missing.
Hope that helps.
very helpful, thank you!!

Pls help, everyone keeps telling me to update all the things because someone worships 4 or something.
What is going on for the ppl who don't know networking?
Basically, when choosing a private encryption key - normally a long string of random characters - in a crucial place for widespread Internet security, some knob just used "4".
What you say is extremely unlikely. No one decided to use 4.
Either the system they had for generating the key was broken, or they accidentally used a test key for a real system.
I think I reworded my post from "decided to use" to "used" just as you posted that correction, with which I agree.
Sounds legit, thanks for the tip.
