user224

joined 3 years ago
[–] user224@lemmy.sdf.org 1 points 48 minutes ago

If you’re okay with abandoning aging parents, why not leave a child up for adoption? Both are, quite frankly, gross concepts

Having children is a choice, and you agree to be responsible for them.
Being born is not.

[–] user224@lemmy.sdf.org 4 points 15 hours ago (1 children)

but with wrong answers (stored in a password manager)

In which case you never need to reset a password to begin with.

[–] user224@lemmy.sdf.org 1 points 1 day ago* (last edited 21 hours ago)

Sorry, that seems to be a registrar, not a registry. What TLDs do you use? For example, Verisign operates .com, .net, .cc and .name.

[–] user224@lemmy.sdf.org 1 points 1 day ago

Oh, hey! Just wanted to remind you that zombo.com has been purchased by someone else and turned into AI slop.

[–] user224@lemmy.sdf.org 7 points 1 day ago (3 children)

why not host your own

I'll first have to research how, but at no point will I consider myself as reliable as some professional provider like Cloudflare.
On the other hand, Cloudflare is kind of becoming the internet with all the centralization. Imagine if Cloudflare and AWS completely went offline at the same time. The internet would be fairly quiet.

[–] user224@lemmy.sdf.org 6 points 1 day ago* (last edited 1 day ago)

This is good EU related info.

Wasn't meant to be. I didn't mention that .eu is only available for citizens, residents and companies in a European Union Member State, Iceland, Liechtenstein or Norway: https://cdn.eurid.eu/assets/terms_and_conditions-2.pdf

And history shows that (a country) exiting the EU means losing the domain name: https://eurid.eu/en/news/update-on-brexit-related-domain-names/


(Not the registrar. E.g., .com TLD is operated by Verisign.)

I wanted a domain for my e-mail. Sounds simple.
But I am a major overthinker, so over the period of past 2 weeks (damn!) I've been deciding between e-mail providers, choosing potential domain names, choosing a TLD (round 1 - by price and looks), looking through registrars, deciding whom to choose for nameservers, and now I am comparing registry operators (TLD round 2).

There are differences, such as who can register a domain, restrictions on domain privacy, and some TLDs like .dev are on HSTS preload list.


Currently, I am mostly looking at EURid with .eu TLD.
What piqued my interest is being able to transfer a domain directly through the registry. So, if a registrar locked me out or shut down, I could still transfer my domain.
From EURid:

From your registrar: Your first point of contact should be your registrar.
From the My .eu platform: You can also issue the transfer authorization code yourself on the My.eu account.
From EURid: This should be done only as a last resort. After proving you are the holder of the domain and cannot obtain an authorization code from your current registrar or via the My .eu platform, you can request an emergency transfer authorization code directly from EURid

Alright.
But I must wonder, how do I prove my ownership?

First sign that this may not be that secure is right on the same page:

Print the form, sign it and send it to us via email at authcoderequest@eurid.eu. If the requester is an organization, please print the form on company letterhead paper or add a company stamp.

OK, the form. Here's the request page. Fields are domain name, first name, last name, job title, email address, and reason for the request.

I generated the form to see what's there. So... is this the security?:

I hereby confirm that I am the rightful holder of the domain name mentioned above, or that I have obtained the legal power to represent the holder, and that all data provided is true and correct. I am fully aware that making a false statement in this matter is considered fraud and may have judicial consequences.

I mean, it doesn't even sound like they collect your signature during the verification, not that a picture provides much security. This is one of the methods:

You can receive a small bank payment (less than one euro) from EURid, which includes a 10-character code that starts and ends with “EU”, with six digits in between (EUXXXXXXEU). After receiving this payment, the domain holder logs in to the My .eu platform and enters the code to verify their registration data.

Either way, it seems this might be mitigated by registry lock:

The Registrar Lock Service will also protect your domain name from accidental changes, but the difference from Registry Lock is that a locked domain name can still be transferred with an authorisation code sent to your My .eu account or an emergency authorisation code received from EURid.

Enough about safety. What about privacy?
The T&C [PDF] prohibits the domain having info of the registrar:

Your registration data must be your own data and must not be that of your Registrar, or of a proxy holder or a representative of a natural person or legal entity who does not meet the eligibility criteria. You may at any time check your registration data via the web-based WHOIS or the secure registrant portal available on our Website.

But it gets a bit better in the WHOIS policy [PDF]:

When the Registrant is a natural person the Registry publishes the Registrant´s e-mail address and language.


Alright. I hope there's someone else who took a similarly overcomplicated route in choosing a domain name.

[–] user224@lemmy.sdf.org 11 points 1 day ago

When the doctor gives you 3 months, but the judge gives you 15 years.

[–] user224@lemmy.sdf.org 23 points 1 day ago* (last edited 1 day ago) (2 children)

Not drugs, but at my workplace (in EU) breath alcohol tests were common. Well, sort of. The managers were supposed to walk around with breathalyzers and test x random employees. But that would be inconvenient, so it got reduced to signing a form.

"Are you drunk?"
"No."
"Can you sign this form stating I tested you?"
"Yes."
"OK, thanks."

Anyway, I guess drug tests are more involved. How are they done?

[–] user224@lemmy.sdf.org 16 points 2 days ago* (last edited 2 days ago) (2 children)

Starlink is for civilian use only.

the restrictions affect the military-grade Starshield service

Starshield leverages SpaceX's Starlink technology and launch capability to support national security efforts. While Starlink is designed for consumer and commercial use, Starshield is designed for government use

https://www.spacex.com/starshield

[–] user224@lemmy.sdf.org 2 points 2 days ago

"Smoking kills."

[–] user224@lemmy.sdf.org 3 points 2 days ago* (last edited 2 days ago) (2 children)

OK, now I am even more interested. dig doesn't return an A record:

$ dig glauca.digital a

; <<>> DiG 9.20.27 <<>> glauca.digital a
;; global options: +cmd
;; Got answer:
;; ->>HEADER<<- opcode: QUERY, status: NOERROR, id: 11516
;; flags: qr rd ra ad; QUERY: 1, ANSWER: 0, AUTHORITY: 1, ADDITIONAL: 1

;; OPT PSEUDOSECTION:
; EDNS: version: 0, flags:; udp: 1232
;; QUESTION SECTION:
;glauca.digital.                        IN      A

;; AUTHORITY SECTION:
glauca.digital.         3600    IN      SOA     ns1.as207960.net. 2bd17d47fafc43aa9be298a1cdfbd0ee.dns.glauca.digital. 1791925047 86400 3600 86400 3600

~~Somehow, it does work in a browser.~~ I tried different DNS servers as well (including NextDNS which I use in a browser), none returns an A record (or AAAA). So, naturally, I am curios what IP the browser uses. Since it clearly works, I tried ping just so that I could see the resulting IP, and figure out where it's coming from.

$ ping glauca.digital
ping: glauca.digital: No address associated with hostname

Great. That makes absolutely no sense at all. Where is Firefox getting the information from?
So I went to about:networking DNS tab. The address field is empty. I am just typing this as I test. It's just cache in my browser.

I guess that would answer on reliability question. At least their nameservers still resolve to IP.


Possibly it would make more sense to ask on the 196 community based on the company's energy.

Anyway, I was browsing EURid's list of registrars, and this company's logo took my attention. However, I can't find any experiences online.

I've checked through their websites, and so far my feelings are a bit mixed. Although most of it is just outdated or somewhat inconsistent bits across their websites.

Things that make me unsure

First and least important is info about one of the people behind the company, "Alfie". Links on the about page are just completely outdated and dead. Website link in docs is at least alive, but also outdated, as can be seen by navigating in manner of URL in docs -> keybase -> GitHub -> newer website.

Second, the "Email us" button on the contact page redirects to a contact form, which really contradicts the text below:

If you want to send us a PGP encrypted email, please use the below key. Remember to attach your own key (as application/pgp-keys), so we can encrypt our reply to you.

That sounded so cool when I've seen it, but what e-mail address?
The contact form is on a "support" subdomain of their other website. This seems to be centered around the contact form, but there is also a "Manage PGP keys" button which redirects to a login page.
Maybe they migrated to that?
But then going to contact page on the domain's second level does show an email, as well as linking to the same contact form.

Third, in the list of services, there's also "Email"... which presents a self-signed certificate. Ignoring that, there's just an "Unknown URL" error page.

We're probably not responsible for this domain.

Lastly, and most importantly, right on ther main page it says:

Proxy registration for .eu

And that's the only mention of that feature. But what is it? If following ICANN's definition...

Proxy Services – Proxy services allow a domain name to keep certain identity and contact details from appearing in public Whois information. The proxy service becomes the registered name holder of record, and its identity and contact information is displayed in Whois data.

...it might be a problem. Because, let's take a look at T&C of EURid (PDF):

Throughout the Term of your Domain Name registration, you must: [...] b. keep your registration data accurate, complete and up-to-date at all times. Your registration data must be your own data and must not be that of your Registrar, or of a proxy holder or a representative of a natural person or legal entity who does not meet the eligibility criteria. [...]

There's also an annoying requirement for tax reasons, but that's not their fault:

In short things are about to get a lot more complicated. We will need to collect at least two pieces of non contradictory evidence about which country you’re resident in, so we can pay the correct tax authority.

And what caught my attention (in a good way)

As I've said, I checked them based on their logo. That's not a usual company logo.

Pricing for .eu TLD is OK.

Their ToS is short.

One button on bottom says "there's no ai here!".

Looking at the about page, this seems to be a small company operated by 2 people.

Looking at their mailing list archive, they've used to have a VPS service, gave shutdown information in advance (though less than 2 months), and set-up a migration route with another provider.
They've also informed about a security incident at one of their registries.

WHOIS privacy includes email forwarding from a funny domain name:

If you do not select it we will generate an anonymous @owowhosth.is email and publish that instead.

On their Mastodon, they describe themselves with

On a mission to make interneting a little easier, join us at http://glauca.digital/. Possibly anarchist, definitely antifascist.

Oh, and speaking of Mastodon, that is listed as one of their services. Based on this disclaimer...

MOBILE APP USERS: if you're trying to sign up with a mobile app go back and select login to authenticate with our SSO.

...it does indeed sound like being their customer includes account on their Mastodon instance. Pretty cool if true.

Also, try whois with their ASN:

aut-num:        AS207960
as-name:        AS-TRANSRIGHTS
descr:          Trans Rights! Hell Yeah!
[...]
remarks:        ----------------------------
remarks:        Hmmmmm tasty routing policies...
remarks:        ----------------------------
 

In the past when deciding between VPN (as in proxy) providers I went with Mullvad because their ToS and Privacy Policy was by far the shortest.

So just the same I now checked all the related links, copy-pasted all the text into Writer (to use as a simple word counter), and found that Cloudflare sits at 22,490 words while Porkbun at 22,554 (excluding contact info).
So that's not helping me make the decision.

The most commonly quoted average reading speed is 238WPM, so that's around 95 minutes each...
...after which I should remember enough to compare them. Or take notes.


It's already both happened to me that I didn't notice I couldn't move a piece without exposing the king or that I won by accident. Had the game not announced this, I wouldn't have known.

And perhaps the opponent might not notice my mistake either. Or it could just be a strategic high-risk scenario, rather than a mistake.


.email TLD is around $25/year, which seems too expensive when .com is less than a half, but it would make it easier to explain why there is no website behind my domain (as I just want something for email).

But there's also more expensive options, so I am curious what you're paying.


Running services, network usage, memory usage, bandwidth, disk I/O, successful logins, whether the thing is even alive, etc...
So far my only method has been "hope and pray".


Currently thinking about either Tuta or Mailbox.org, but to be honest, I don't even know many providers.
Something I do not like is limit on number of addresses with a custom domain. Mailbox is at least a bit reasonable with 50 on Standard, but Proton's 10 on Mail Plus is disqualifying for me.

Tuta has unlimited number, but doesn't support PGP.

So I plan to check out whatever you guys use.


Brain-based management is getting too exhausting, and isn't even fully possible with a larger quantity of online accounts.


Yesterday, someone topped up my number with a small amount of credit (pay-as-you-go), and activated unlimited monthly mobile data package.

I still have a data plan (prepaid data, postpaid calls and texts) on my main SIM expiring in a week.

I haven't used any of it (on secondary, of course), and contacted my carrier's tech support stating these appeared unexpectedly. Their response was "We would like to inform you that the credit on your phone number was topped up at a point of sale. The unlimited package was later activated at the same point of sale."
And? Was the tech support person just trying to imply it was likely paid for in cash and I just shouldn't care because they couldn't refund it anyway?

Anyway, one annoying thing about this is that it also activated automatic renewal, so if I wasn't using the number for a few months, I wouldn't notice my remaining credit automatically draining.
Hell, if I had registered for their online account, it would even possibly pay that directly from my debit card on renewal.


(Images are hosted on catbox.moe with a total size of 1.9MiB - your data plan will be fine)

Following Android docs, unlocking a bootloader should be as simple as enabling that option in developer settings, and issuing fastboot flashing unlock command in the bootloader.

But not all manufacturers like that.
So, here's the fuckery I went through.

Obtaining Mi Unlock tool

That one comes from here: https://en.miui.com/unlock/download_en.html
Which also links to these steps: https://new.c.mi.com/global/post/101245

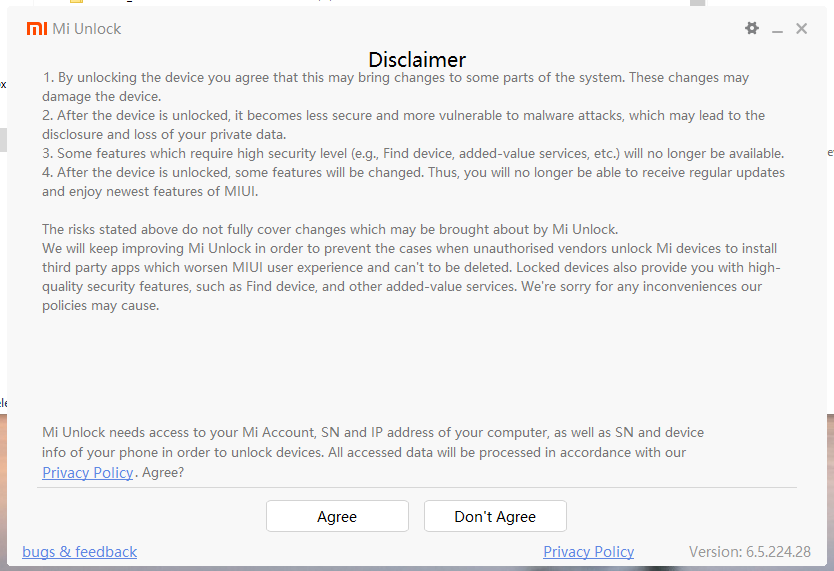
First run

Disclaimer + privacy policy link
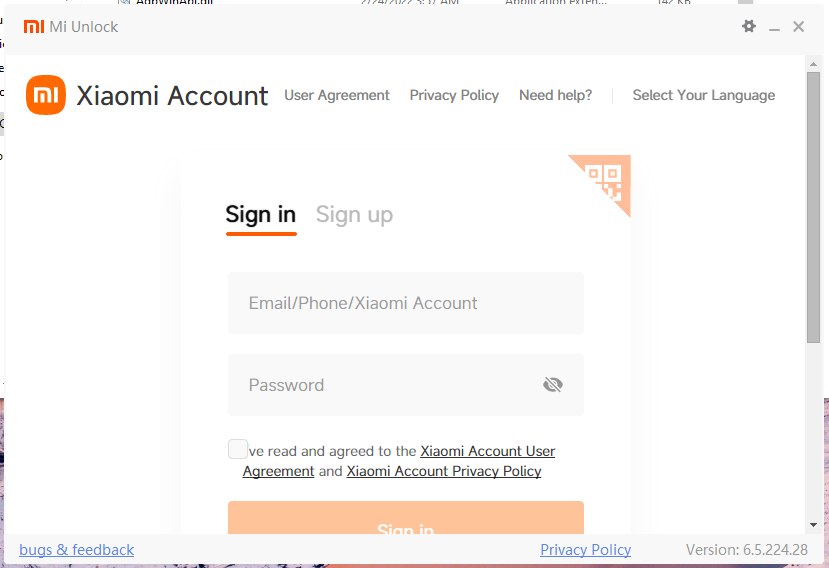
And we need an account.
Log-in screen

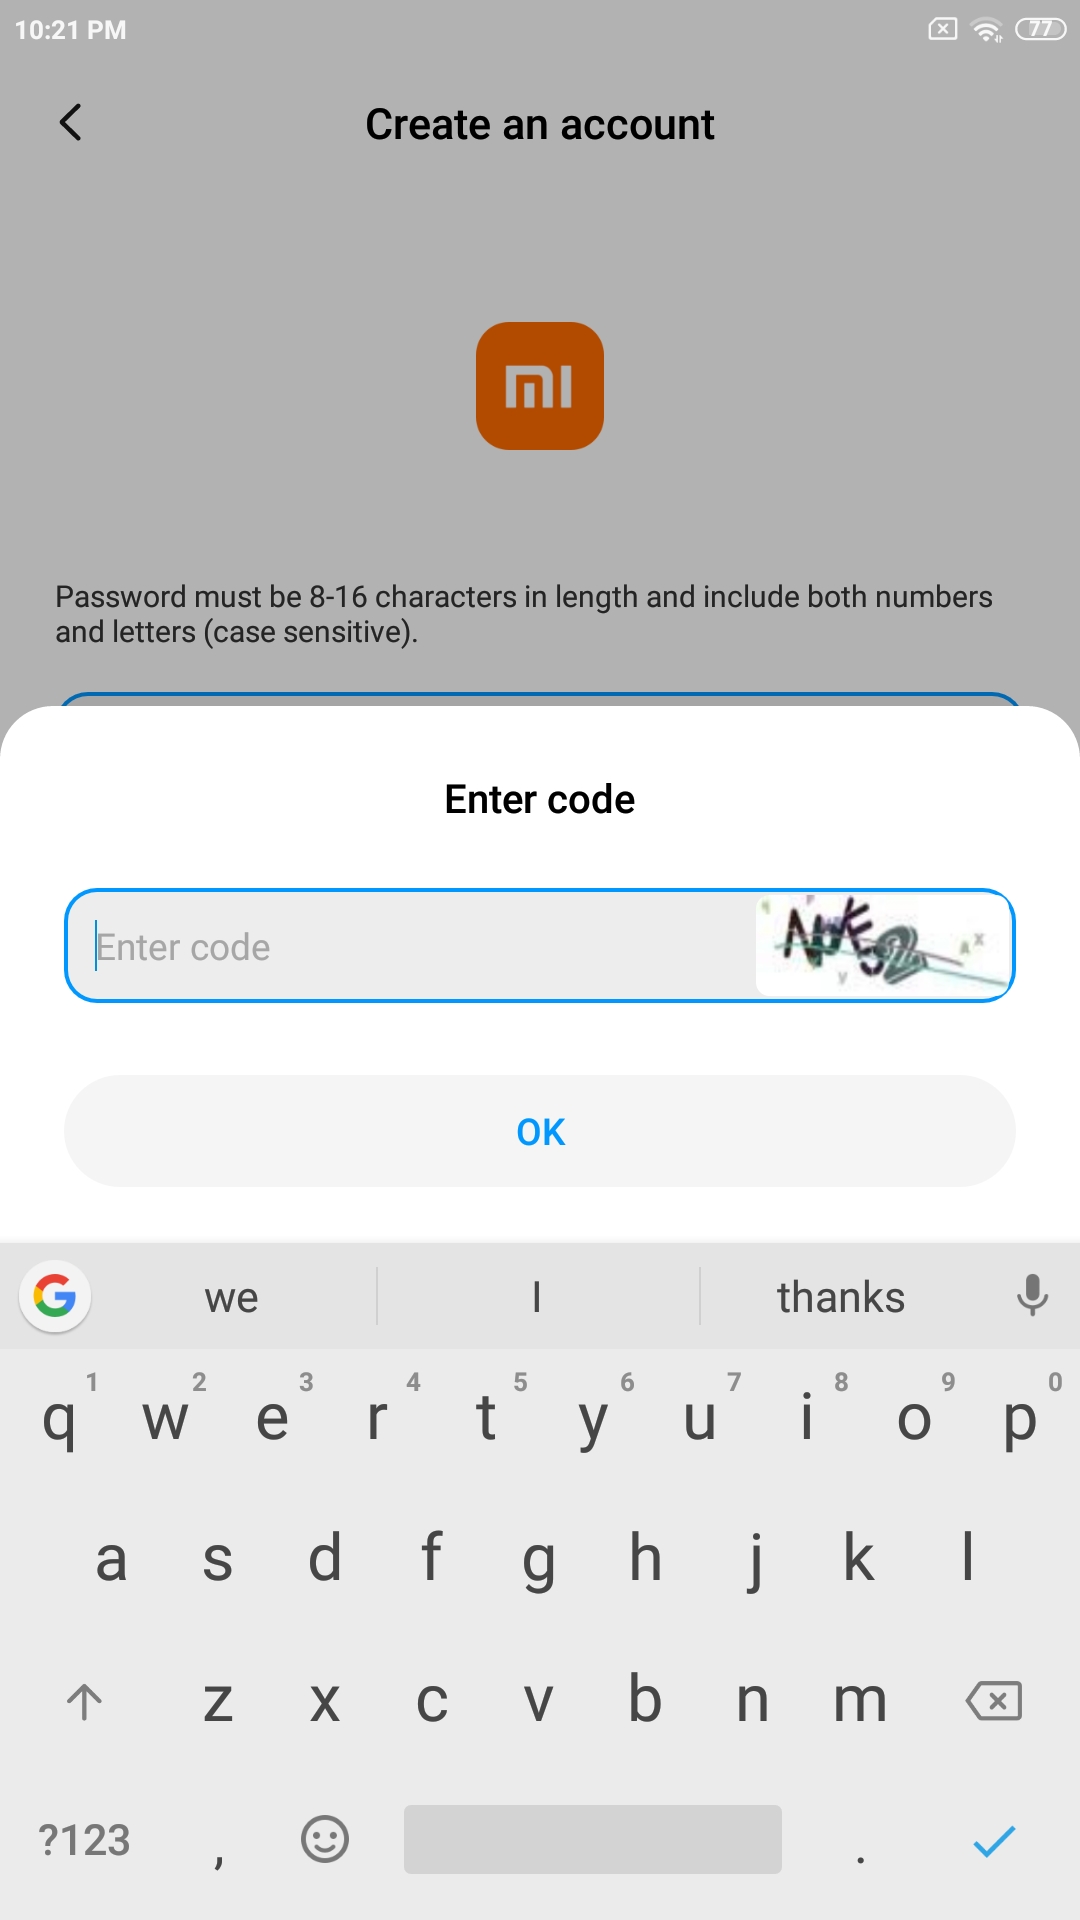
Account creation

Since I'll need it on the phone as well, I decided to create the account from there.
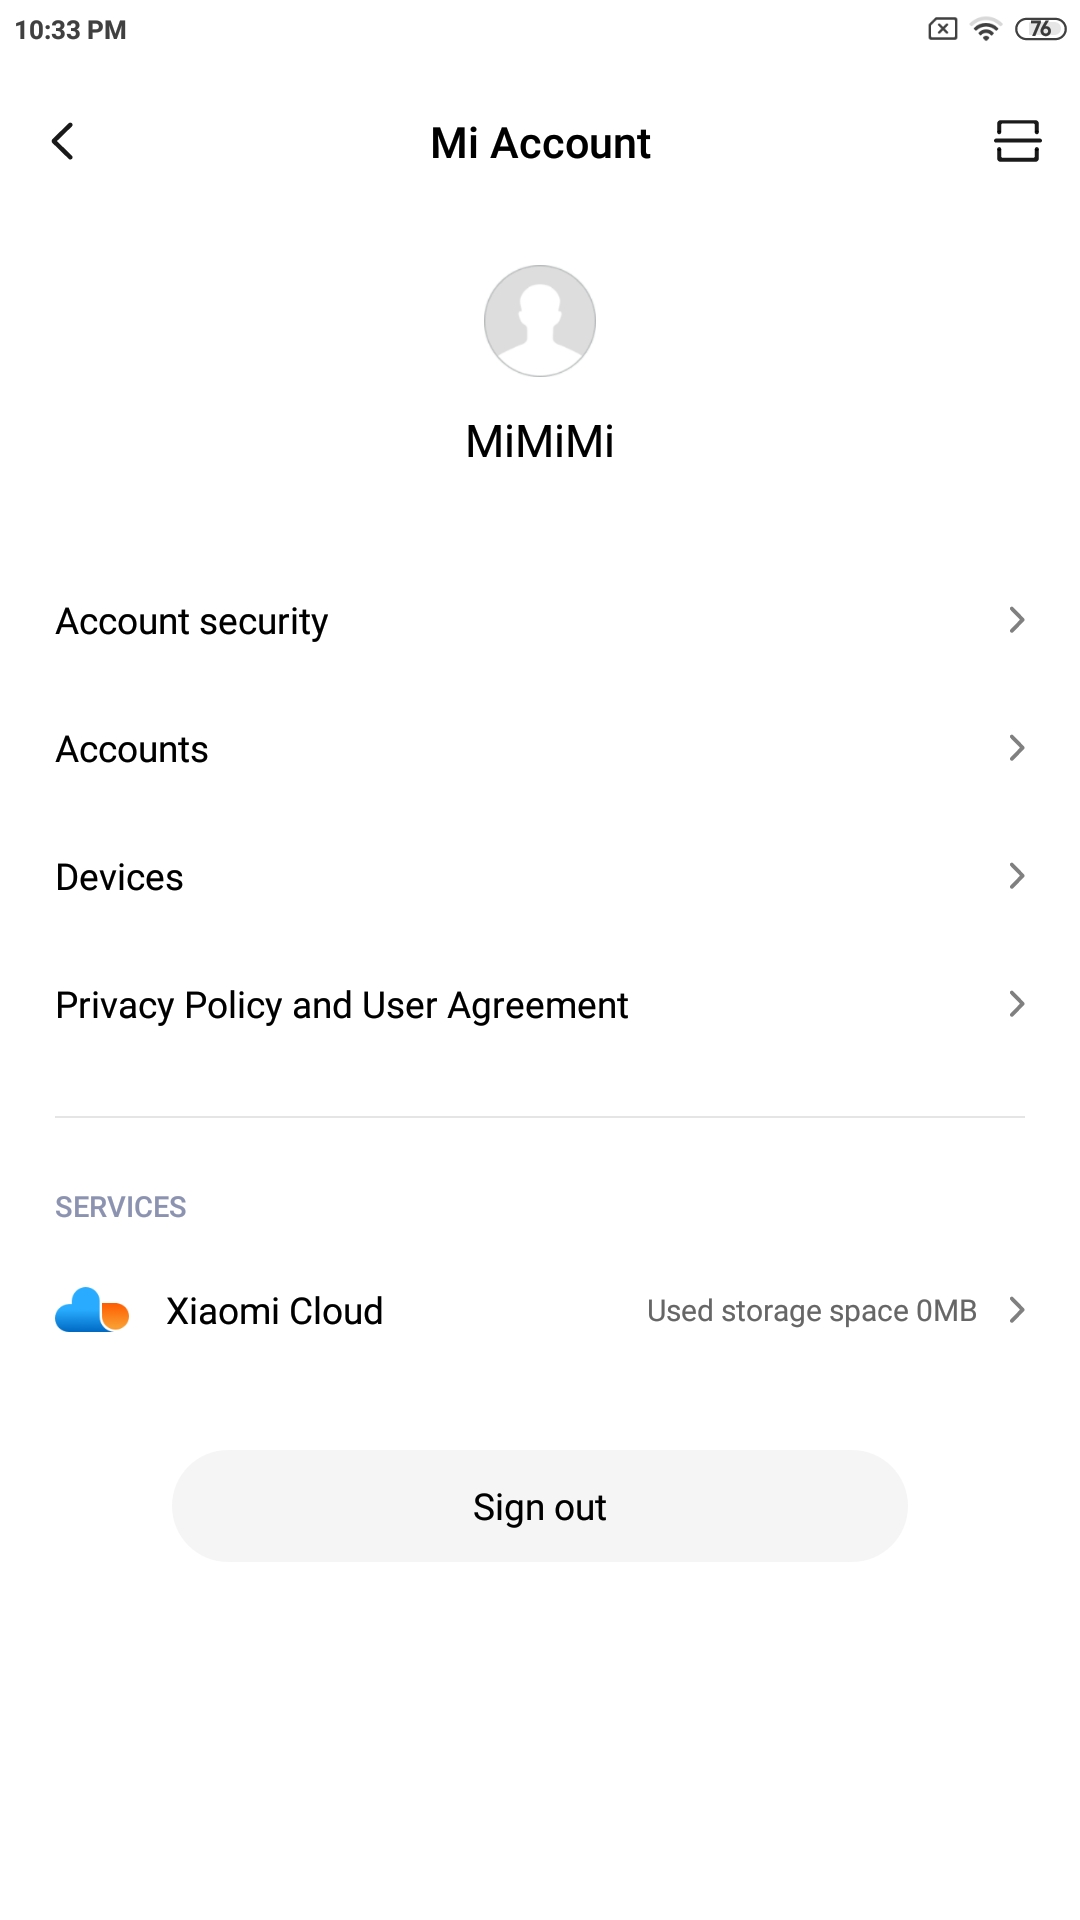
Simple captcha Account page
I've used e-mail + password for sign-up.
There was also a confirmation e-mail sent to me, nothing special so far.

Logging into Mi Unlock - First roadblock

After entering e-mail + password, it fucks up with a blank verification page.
Blank verification page
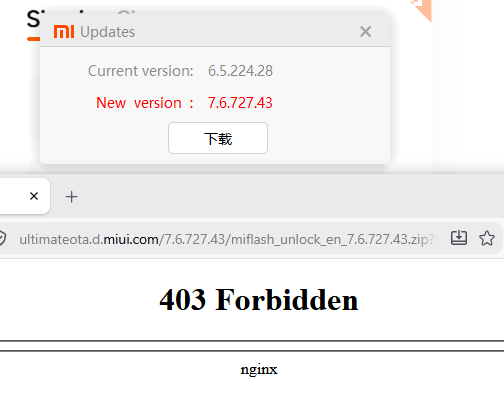
This was also reported by someone on XDA, with a solution to update.

Mi Unlock updaten't

403 Forbidden
I've tried both with and without a VPN, no luck. Some people reported the same issue when I searched around.

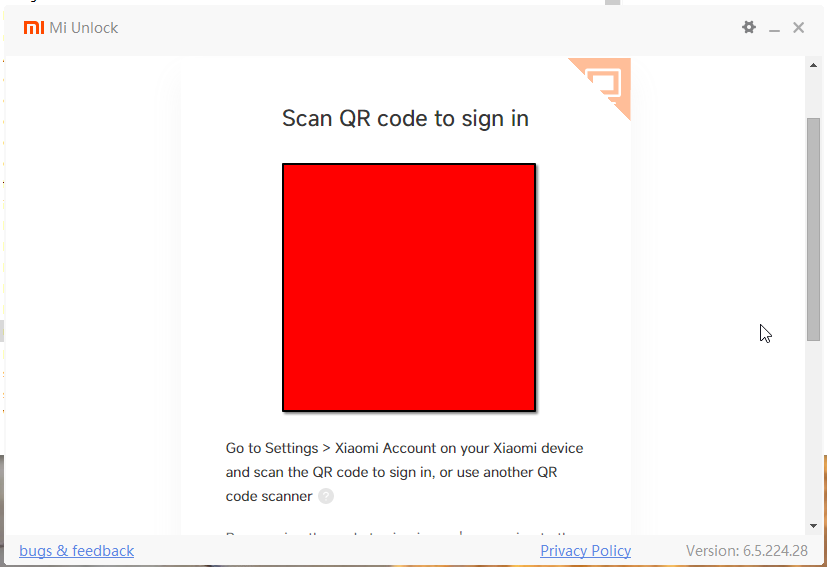
Workaround - QR code login from phone app

QR code login page
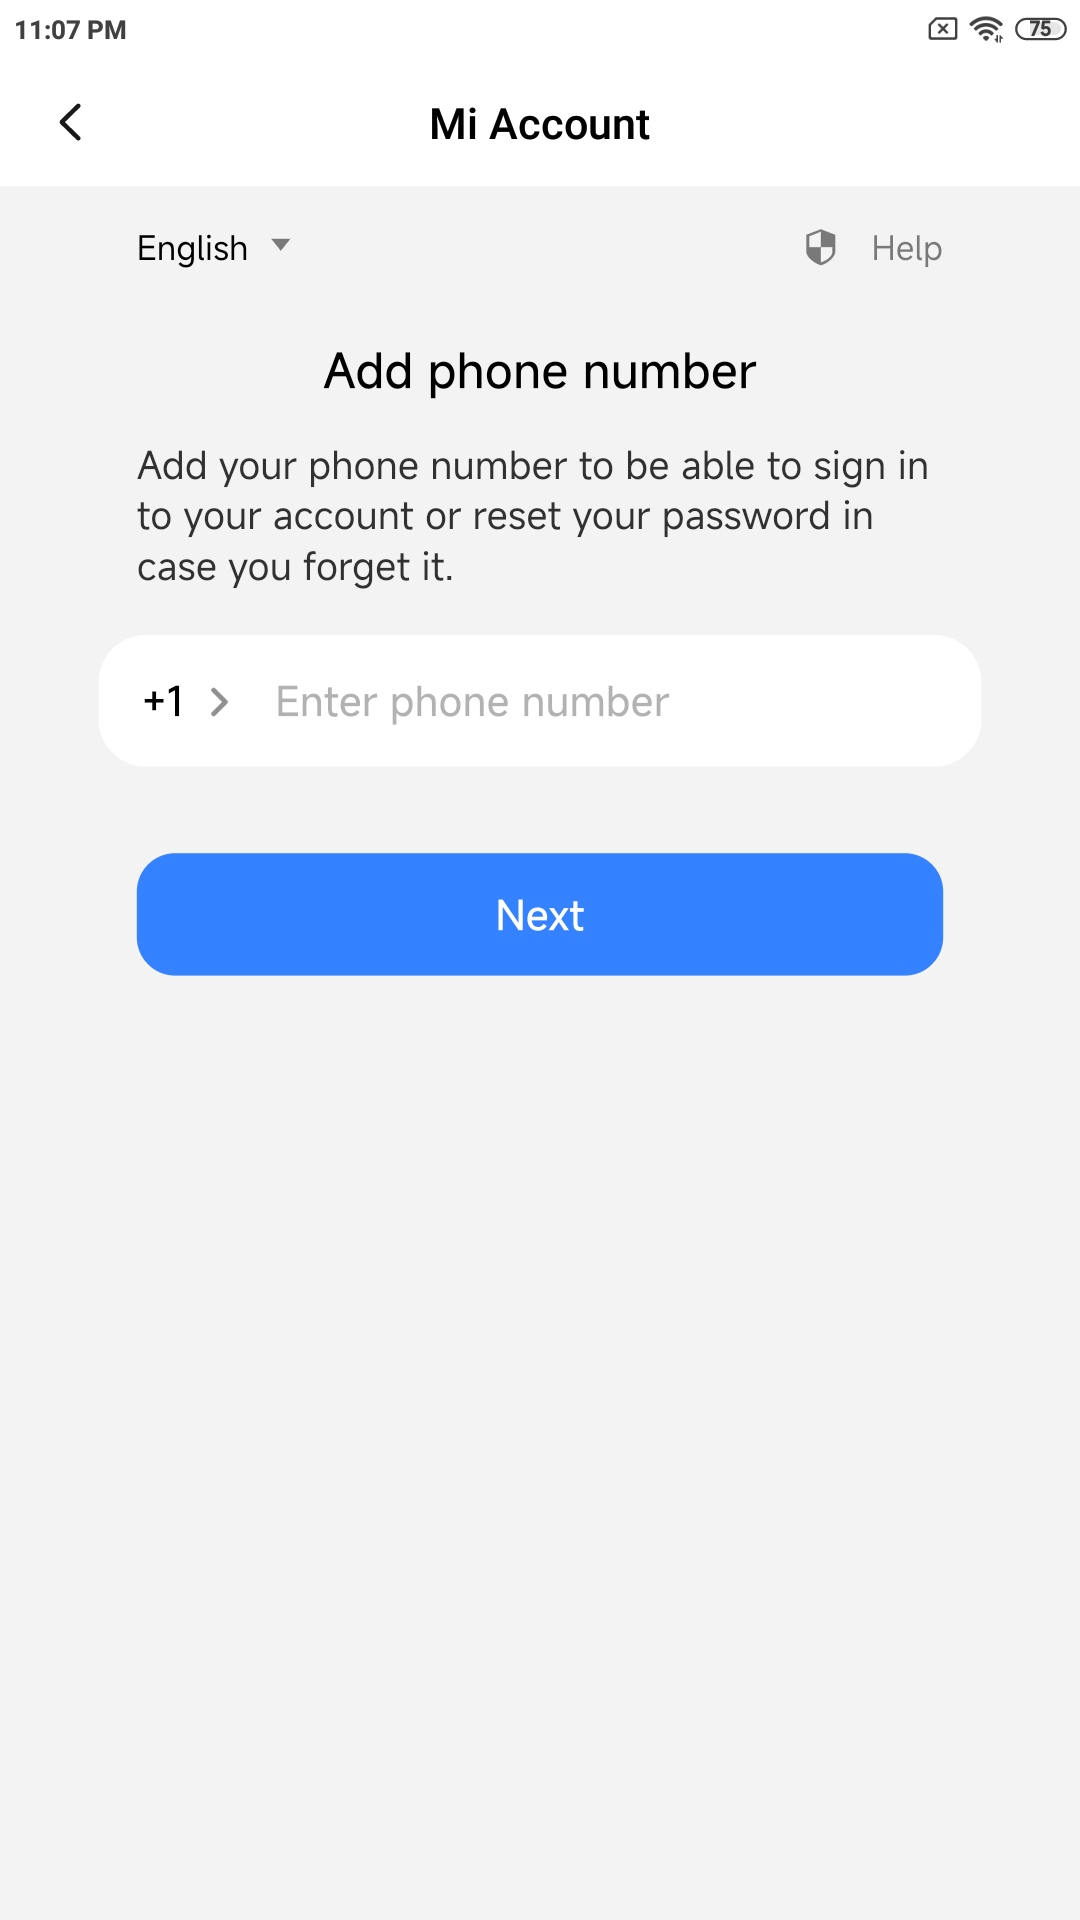
Of course, this needs more private data - a phone number, because why not?
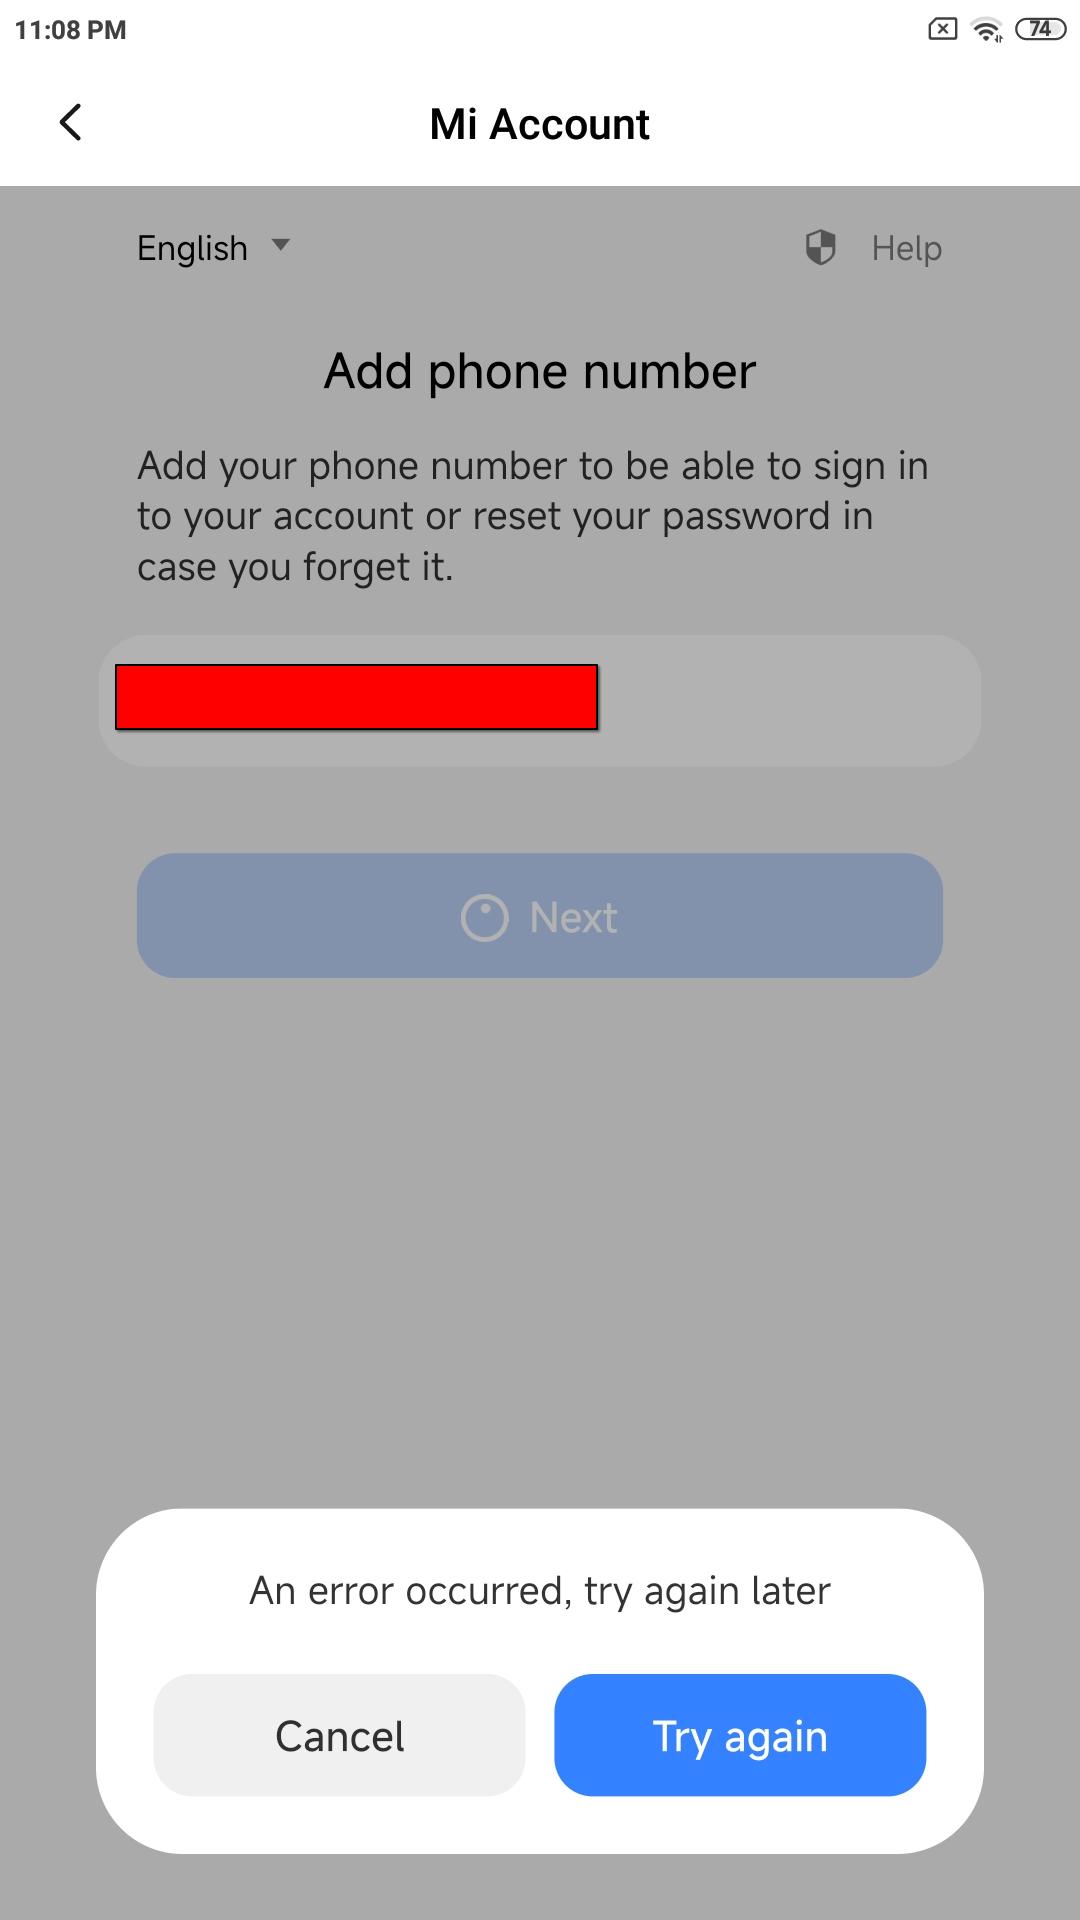
And of course, it also does not fucking work.
Phone number prompt Error when entering phone number

Entering phone number in browser

This worked. But the phone app still didn't like me.
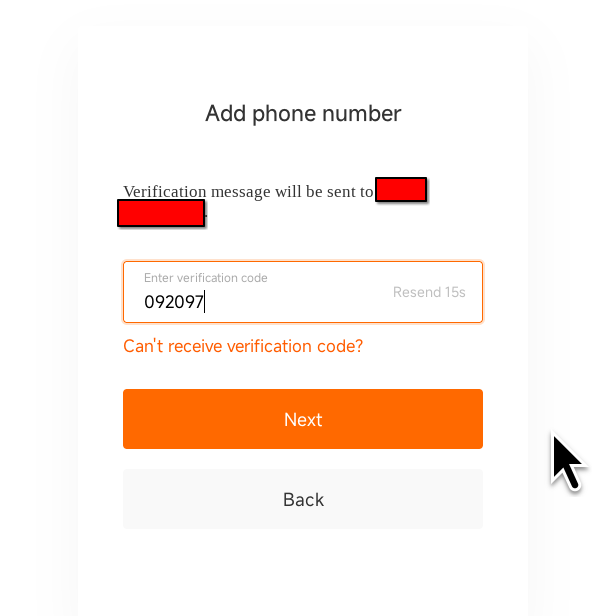
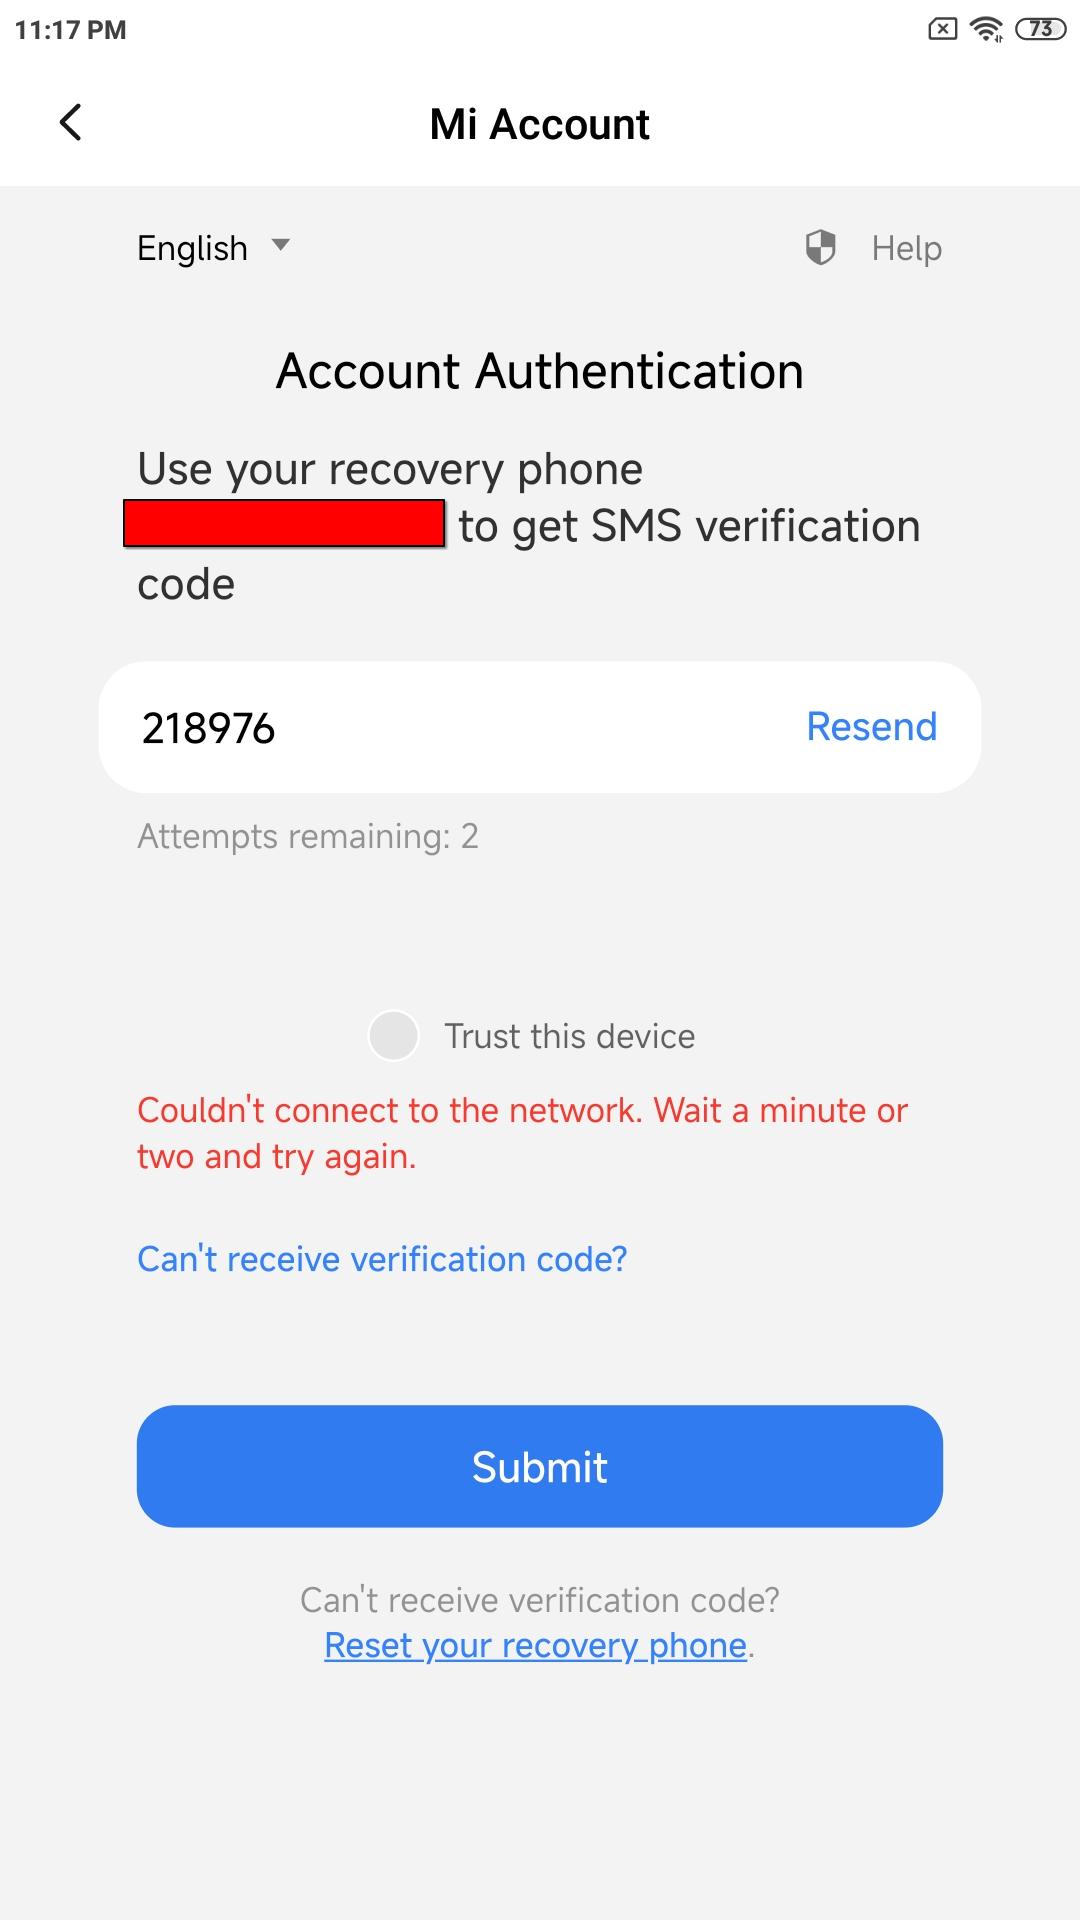
Phone number confirmation prompt Phone number confirmation error on phone
Do notice the "attempts remaining", this will be important later.

Workaround - QR code: Electric Boogaloo

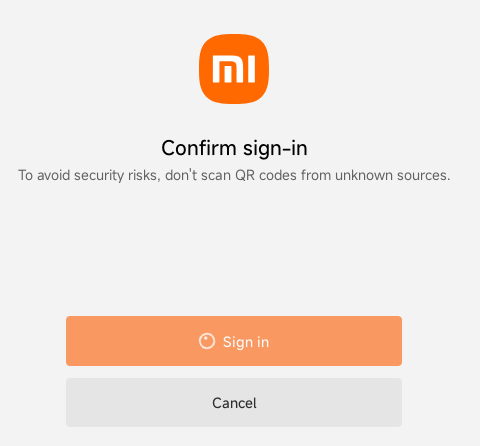
The QR code actually contains a URL, so let's open it in a browser.
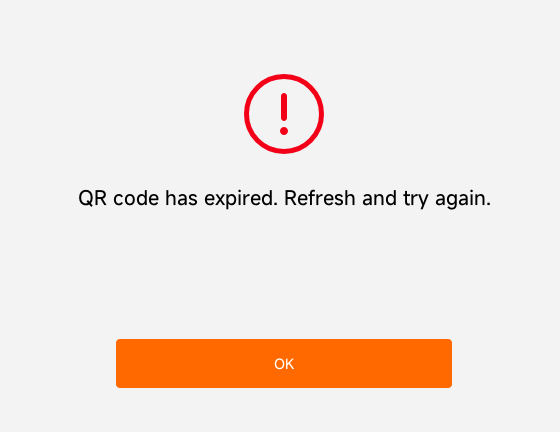
QR code expired
Well, fuck. Let's do that again.
Success
And we are in.
Unlock page

Binding phone to Mi Account - More data collection

I thought the problem above (gray unlock button) was the phone not yet being "binded" to the account, so I skipped to this step.
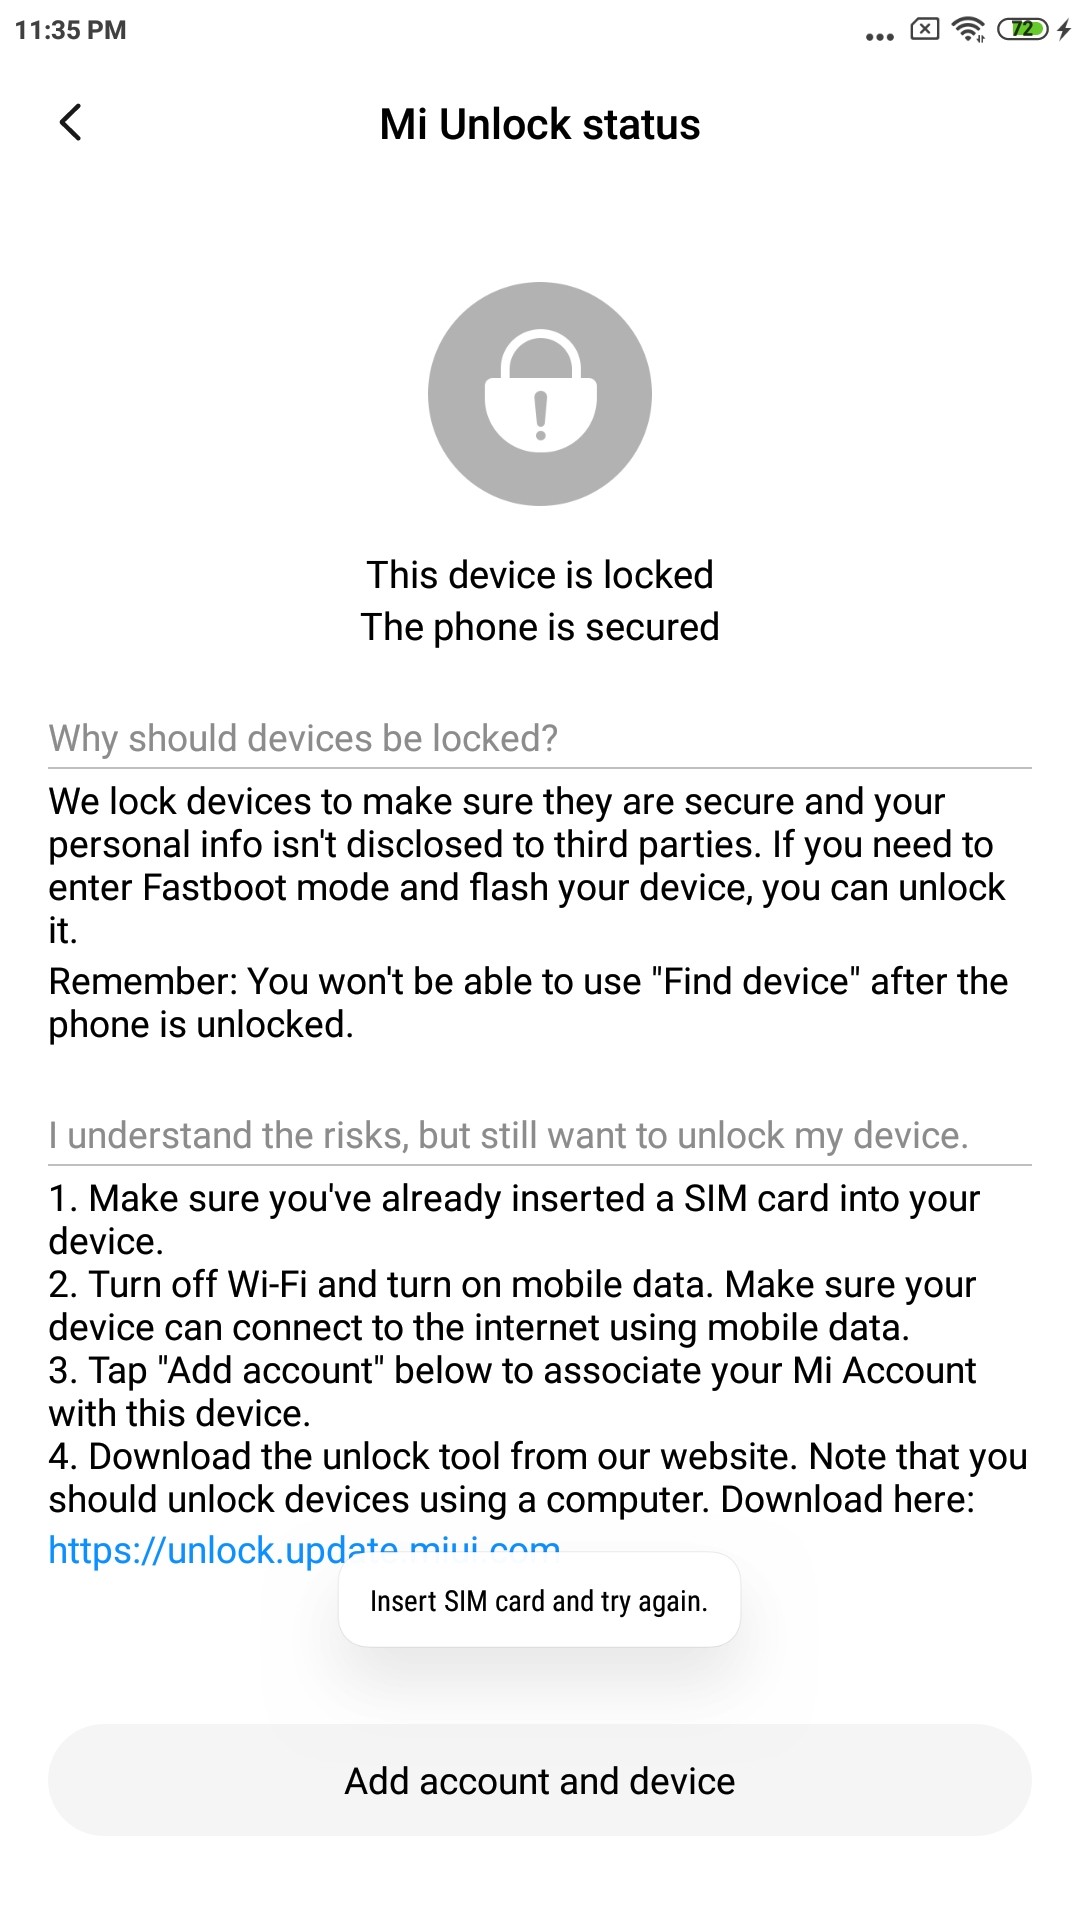
Requirement of sim card and mobile data
So I inserted a SIM card, but they didn't lie. It really requires mobile data. I even tried Bluetooth network as someone else suggested.
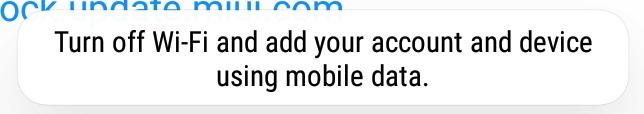
Warning/error about mobile data requirement
This was a bit of a problem as I used a burner SIM with no data.
Random data eSIM on removable eUICC (9esim V3) was able to help with this.
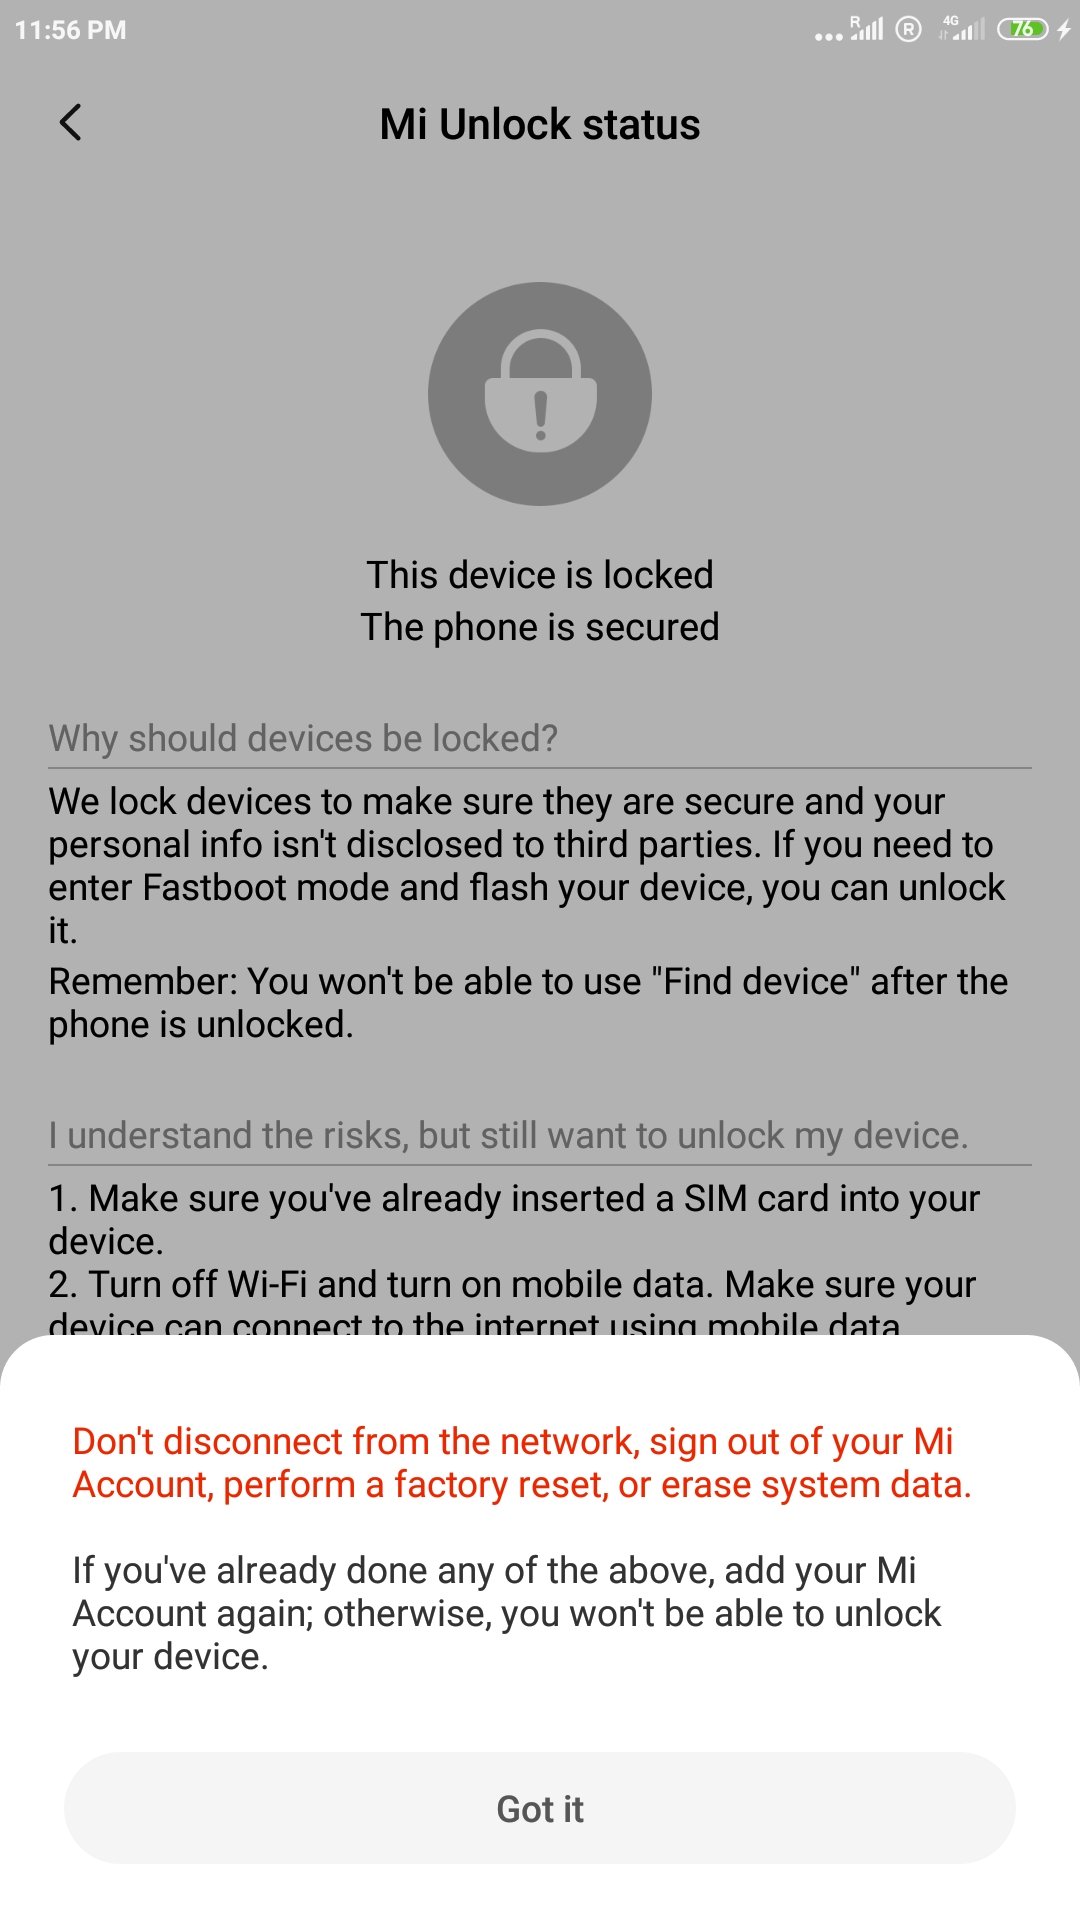
Account binded

Back to Mi Unlock - SMS rate limit

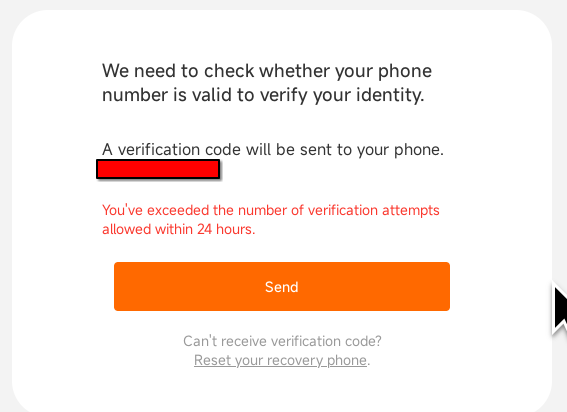
Come back in 24 hours
It seems there's a limit of 3 SMS codes per 24 hours outside of China.
Screenshot of that info

Back the next day - Episode: Windows drivers

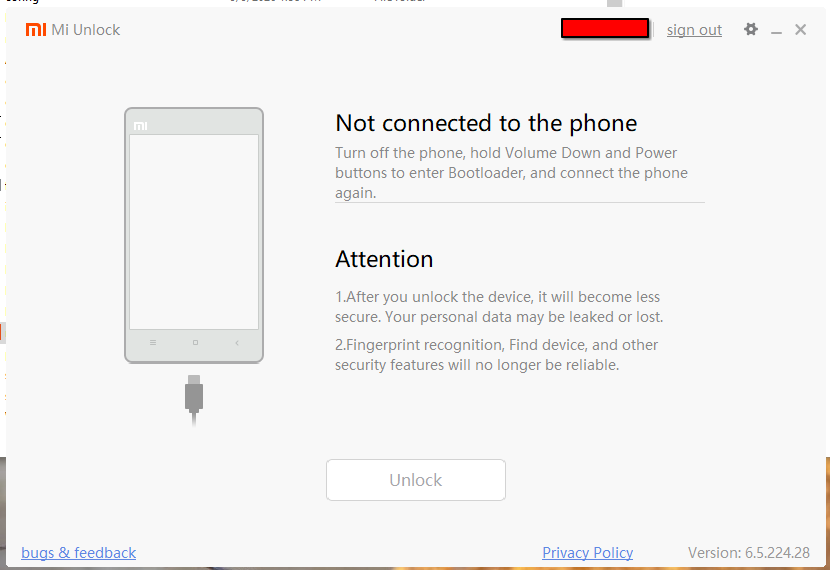
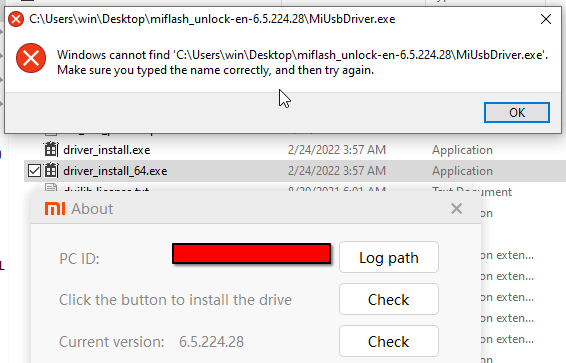
The Mi Unlock tool should include the USB drivers, but something's fucked up there.
File not found
Someone on XDA mentioned one of the 2 driver files can be renamed to the required filename, because let's ship a broken tool.

So I did that: driver_install_64.exe -> MiUsbDriver.exe
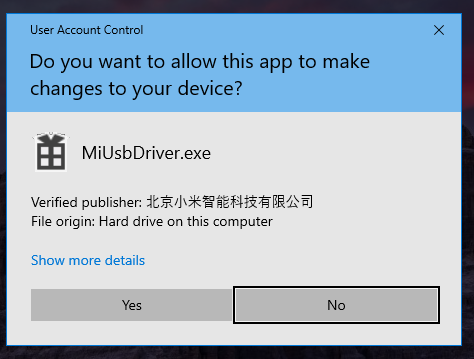
This now shown Windows installation prompt.
Confirmation window

But why yes, it did not work.

So, I downloaded the drivers from Google, and tried following their instructions.
So that did it, right? Nah. Windows wouldn't find the driver.

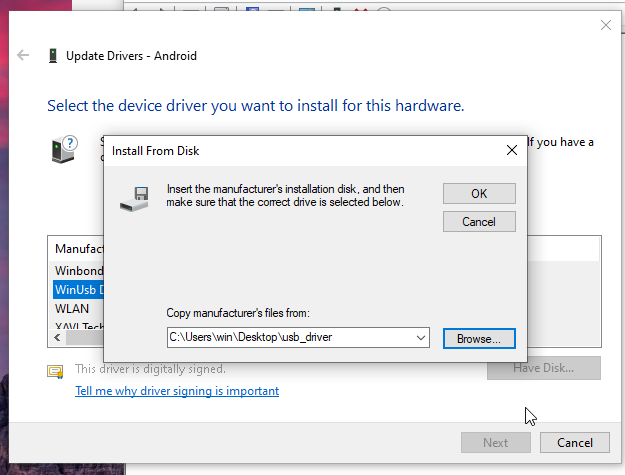
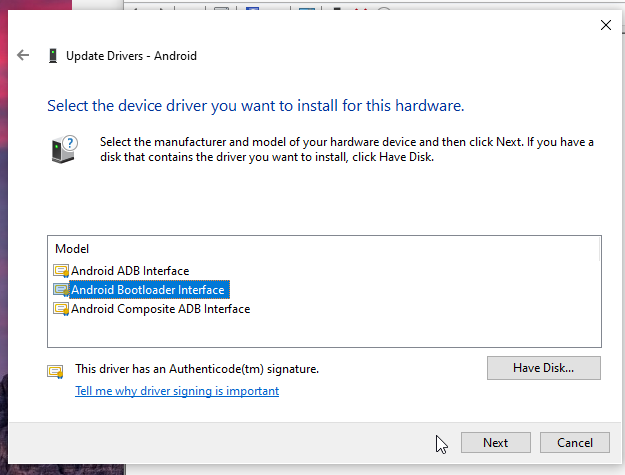
The solution was following someone's Reddit comment.

Choose the option that says 'Let me pick from a list of available drivers on my computer', then browse to and select the file named android_winusb.inf. From there, you'll be able to choose 'Android Bootloader Interface' to install.

Choosing "install disk' Choosing the driver

For comparison, on something like Arch Linux, this is a matter of extremely hard and time-consuming sudo pacman -Sy android-tools. /s

Reaching the fruit

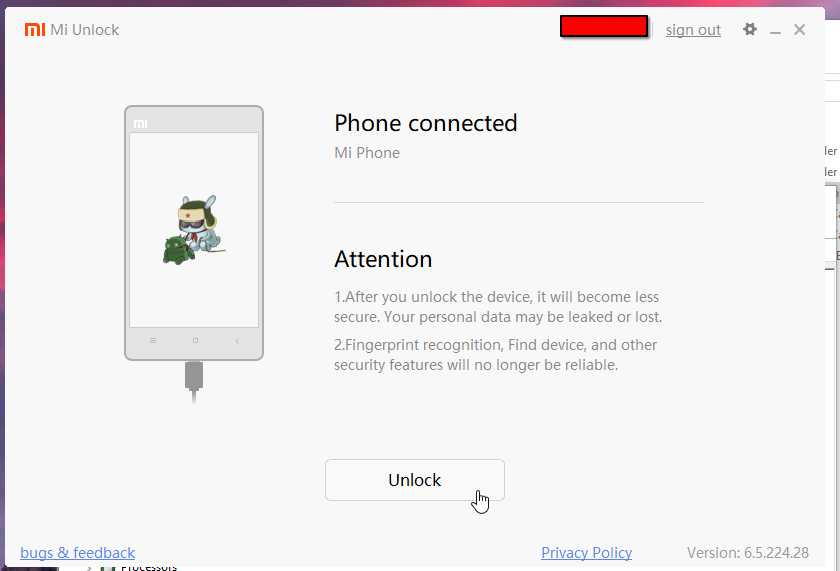
The device is finally recognized.
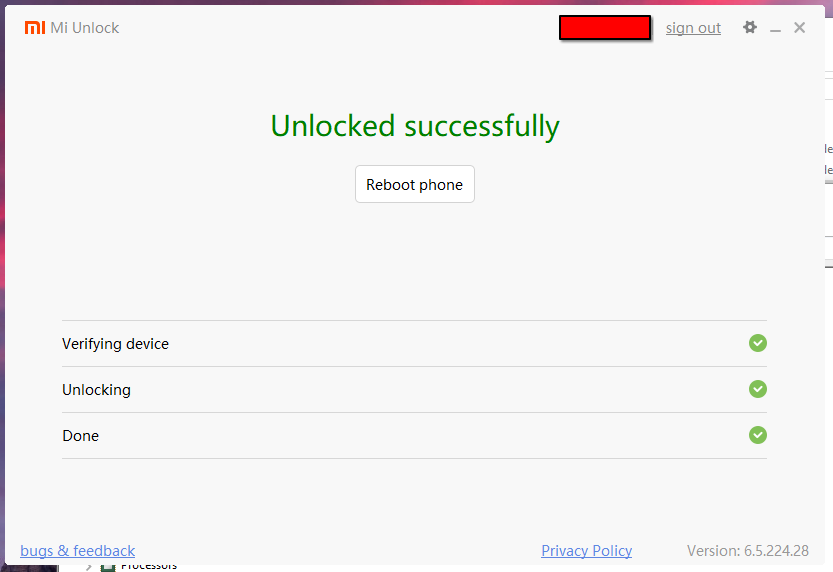
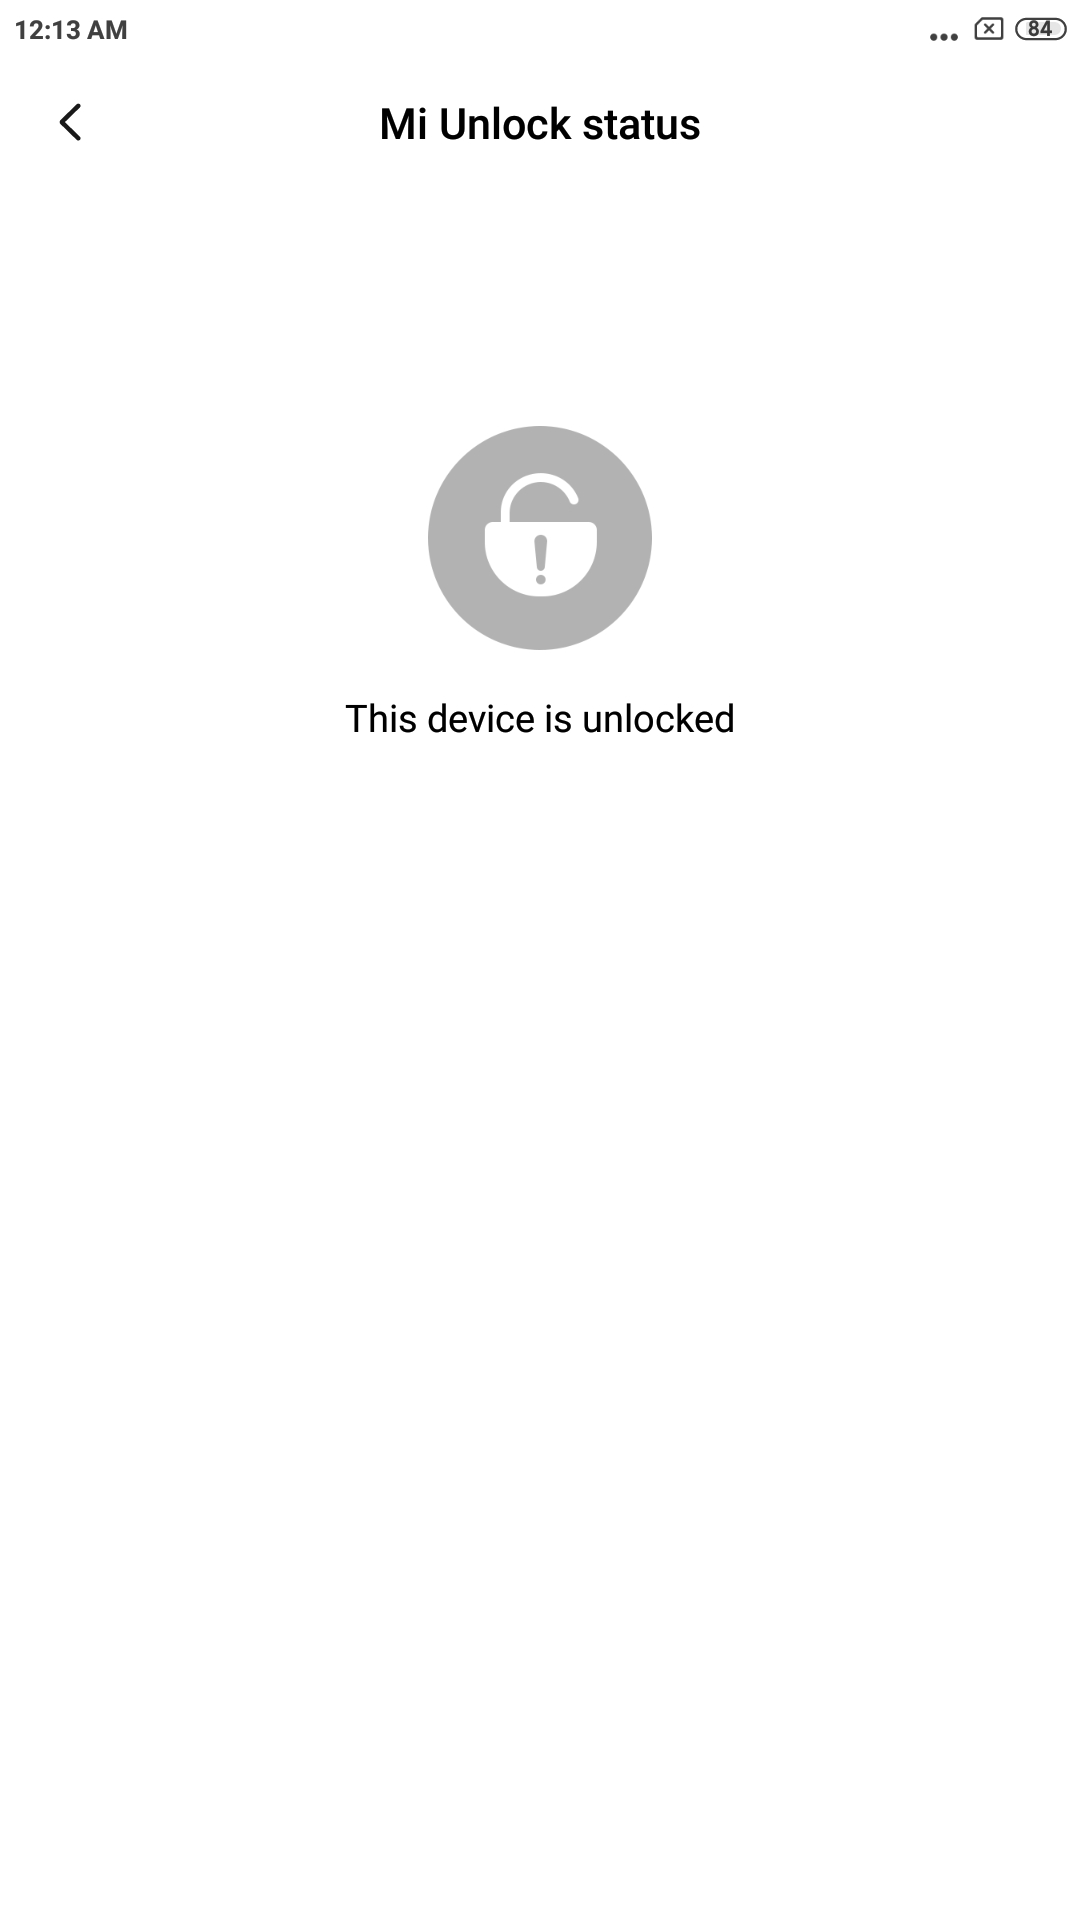
Unlock button turned friendly Unlock success
And there we go.
Unlock confirmation on device

And the final step:
Account deletion

211
submitted 1 month ago* (last edited 1 month ago) by user224@lemmy.sdf.org to c/linux@lemmy.ml
 

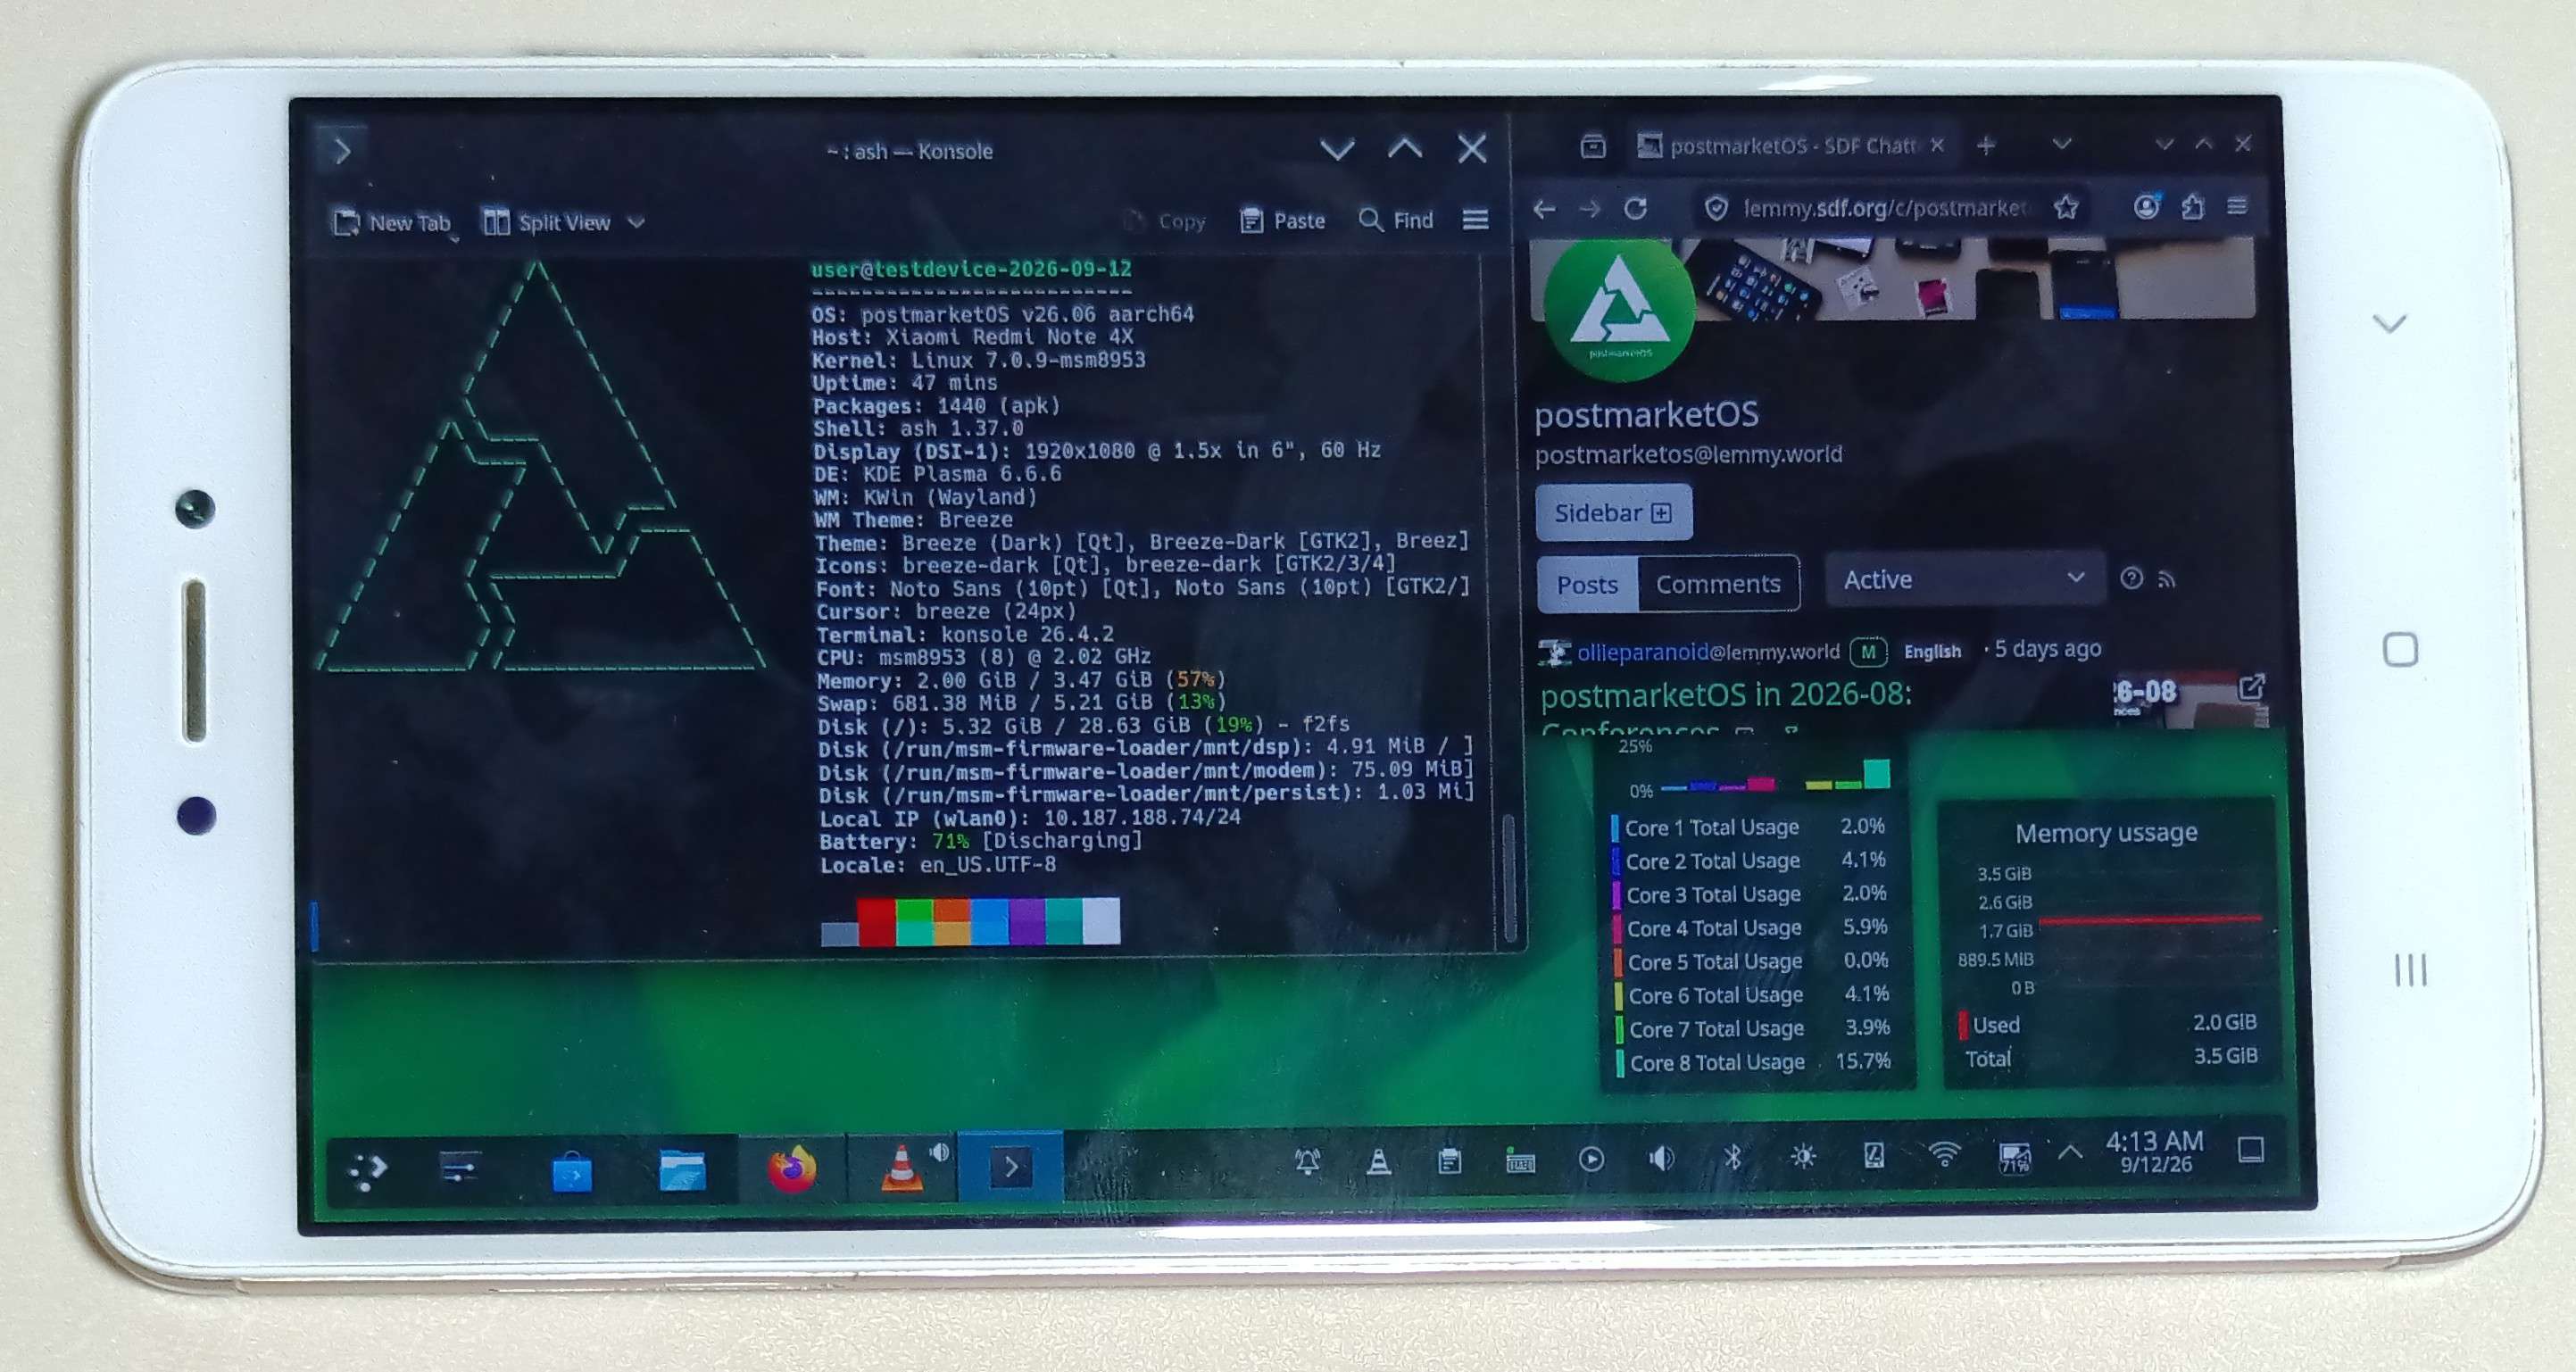
Hardest part?

Unlocking the bootloader. Because it's Xiaomi. I have screenshots from the whole process, but that's more of a thing for "mildly infuriating" community.
Fun fact: Xiaomi doesn't even allow installing APKs via ADB without Mi account...

Why is it running plasma-desktop?

It's the first UI I tried. I've used it with a touchscreen before, and it worked well.
I've also tried installing both plasma-mobile and plasma-desktop, but the configurations seem to clash.
Also, when I use Android I always increase DP in developer settings to >600 which switches some UI elements to tablet mode. I prefer more things on the screen.

plasma-mobile vs plasma-desktop

Apples and oranges, yes, but I'll compare them. I am allergic to apples, but not oranges. Wait, that's not what I was talking about...

Nice things in plasma-desktop

  • Sleep works (dmesg reports s2idle).
  • More powerful UI (proper desktop).

Nice things in plasma-mobile

  • Extra buttons in Konsole (tab, arrows, ctrl).
  • Screen can be locked and turned off.
  • Existing buttons on phone are automatically mapped to navigation in Plasma.

Bad things about plasma-desktop

  • Even if I set power button to "Turn of screen", it immediately turns back on.
  • Awful CLI experience without needed buttons.
  • Pressing back and home buttons causes awful noise on headphone output.

Bad things about plasma-mobile

  • Sleep isn't available as power option. systemctl suspend seems to properly put it into sleep based on kernel logs, but pressing button first time won't do anything, while causing a reboot when pressed the second time.
  • While phone's buttons are mapped, I didn't find a setting to hide on-screen buttons, so you just get each button twice.

Running without modifying anything (aside from bootloader unlocking)

I didn't yet want to modify anything on the device, so I just flashed PostmarketOS to SD card.
The device is then booted through a computer using fastboot boot with lk2nd bootloader image.


Miscellaneous

This section is just about me being dumb.

I have no idea about what's going on during the boot process.
There's 49 partitions on the internal storage, I don't know what they're all used for, nor how data is loaded from them.

Partition table

Device        Start       End  Size Attrs   Name
 1           131072    303103   84M GUID:60 modem
 2           393216    393217    1K         fsc
 3           393218    393233    8K         ssd
 4           393234    394257  512K         sbl1
 5           394258    395281  512K         sbl1bak
 6           395282    396305  512K         rpm
 7           396306    397329  512K         rpmbak
 8           397330    401425    2M         tz
 9           401426    405521    2M         tzbak
 10          405522    406033  256K         devcfg
 11          406034    406545  256K         devcfgbak
 12          406546    439313   16M         dsp
 13          439314    442385  1.5M         modemst1
 14          442386    445457  1.5M         modemst2
 15          524288    524351   32K GUID:60 DDR
 16          524352    527423  1.5M GUID:60 fsg
 17          527424    527455   16K GUID:60 sec
 18          655360    677887   11M         splash
 19          786432    788479    1M GUID:60 aboot
 20          788480    790527    1M GUID:60 abootbak
 21          790528    921599   64M GUID:60 boot
 22          921600   1052671   64M GUID:60 recovery
 23         1052672   1054719    1M GUID:60 devinfo
 24         1054720   7346175    3G GUID:60 system
 25         7471104   7995391  256M         cache
 26         7995392   8060927   32M         persist
 27         8060928   8062975    1M         misc
 28         8062976   8063999  512K         keystore
 29         8064000   8064063   32K         config
 30         8064064   8588351  256M         oem
 31         8650752   8650815   32K GUID:60 limits
 32         8781824   8782847  512K         mota
 33         8782848   8784895    1M         dip
 34         8784896   8850431   32M         mdtp
 35         8850432   8851455  512K         syscfg
 36         8851456   8859647    4M         mcfg
 37         8912896   8913151  128K GUID:60 lksecapp
 38         8913152   8913407  128K GUID:60 lksecappbak
 39         8913408   8913919  256K GUID:60 cmnlib
 40         8913920   8914431  256K GUID:60 cmnlibbak
 41         8914432   8914943  256K GUID:60 cmnlib64
 42         8914944   8915455  256K GUID:60 cmnlib64bak
 43         8915456   8915967  256K GUID:60 keymaster
 44         8915968   8916479  256K GUID:60 keymasterbak
 45         9043968   9044479  256K         apdp
 46         9044480   9044991  256K         msadp
 47         9044992   9045007    8K         dpo
 48         9045008  10748943  832M         cust
 49        10748944 122142686 53.1G         userdata

If I collected info correctly, BootROM loads whatever SBL is, which then loads whatever ABOOT is (which probably includes fastboot), which then decides what to load next (recovery, boot).

But how?
Does it look at the partition table for the names/UUID, or does it look for disk offsets? (There are suspicious holes between partitions.)
If the former, I could re-partition it.
If the latter, I'd be fucked.

Anyway, when it comes to backups, I first erased cache and userdata (fastboot erase), booted TWRP, and cat the internal storage over ADB shell, storing it as a sparse file. It takes up just 3.3GiB.
I also checksummed the storage and image file for verification.

I also tried to extract the stock recovery into Android boot image without extra data after it.
I don't know how to determine the real size, so I used unpack_bootimg and mkbootimg to get the original image, rather than whole partition.
The checksum of re-created boot image was different to original truncated partition image, but upon closer inspection with xxd and diff, this was just a difference in header:

00000010: 68c2 4f00 0000 0081 0000 0000 0000 f080  h.O....... | 00000010: 68c2 4f00 0000 0081 0000 0000 0000 0000  h.O.......

But I found it might indeed be a good idea to just keep a full image backup. After a bunch of NULLs, there's more data.
file doesn't recognize it, but running strings on it reveals readable text:

California1
San Narciso1
Yoyodyne, Inc.1
Yoyodyne Mobility1
Yoyodyne1#0!
yoyodyne@example.com0

Indeed, it seems this is a certificate: https://source.android.com/docs/core/ota/sign_builds#signatures-sideloading

Anyway, I am once again getting reminded it might be good to learn assembly (ARM in this case). The content of sbl1 and aboot seems to be an ELF, so I might be able to pop it into Ghdira, and try to figure out what it's doing.
Maybe. I don't know, I have the most stupid of ideas usually.

view more: next ›